
Organizations that embed security integration across every stage of their DevOps pipeline reduce code vulnerabilities by more than 40 percent and close the gap between delivery speed and compliance. Yet most enterprises still treat security as a final checkpoint rather than a continuous discipline, and that single decision quietly undermines every efficiency gain DevOps promises. If you are a CTO, CIO, or engineering leader responsible for both velocity and risk, this article explains why security integration is the defining difference between a DevOps program that scales and one that stalls.
Why Security Integration Remains the Hardest Part of DevOps?
DevOps transformed software delivery. Continuous Integration and Continuous Delivery (CI/CD) pipelines accelerated release cycles, reduced manual handoffs, and improved team collaboration. But speed without embedded security created a new class of enterprise risk.
Surveys consistently show that security concerns rank among the top barriers to DevOps adoption at scale. The core tension is structural. Traditional CI/CD pipelines were designed around delivery speed, and security operations were managed separately, reviewed late in the cycle, or deferred entirely. When a vulnerability surfaces in production, the cost of remediation is exponentially higher than catching it at the code commit stage.
This is the business problem Secure DevOps, also called DevSecOps or SecDevOps, was designed to solve. And for organizations that implement it correctly, it works. For those that treat it as a rebranding exercise, the gaps remain.
Connect with Our DevOps Security Expert
What SecDevOps Actually Means and Why Definitions Matter
SecDevOps, Secure DevOps, and DevSecOps are used interchangeably, but they all describe the same strategic principle: security is not a phase. It is a property of the entire software delivery lifecycle.
When enterprises integrate security practices into every stage of the pipeline, including planning, coding, building, testing, deploying, and monitoring, they create a system in which vulnerabilities are caught early, compliance is continuous, and remediation costs remain low. Organizations that have made this shift report a decline in code vulnerability rates of more than 40 percent compared with teams using traditional, siloed security reviews.
The distinction that matters most to senior leaders is this: Secure DevOps is not a tool purchase. It is an operating model change that requires alignment across culture, process, and technology.
For a broader look at how DevOps services enhance development and delivery, the methodology’s fundamentals provide important context before diving into the security layer.
The 6 Most Commonly Reported Gaps in Secure DevOps Implementation
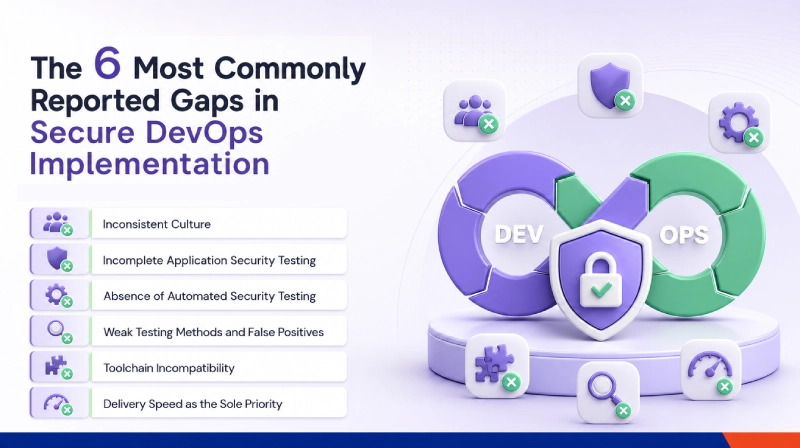
Enterprise teams that report frustration with Secure DevOps implementation are not failing because security is too complex. They are failing because they are attempting to bolt security onto a pipeline that was not designed to carry it. Industry surveys point to 6 recurring gaps.
1) Inconsistent Culture
Secure DevOps requires consistent, organization wide adoption. When security practices are applied by some teams but not others, coverage is partial, and risk is unpredictable.
2) Incomplete Application Security Testing
Only 50 percent of organizations report fully integrating application security testing elements into their CI/CD workflows. The other half are shipping code through pipelines with blind spots.
3) Absence of Automated Security Testing
Manual security reviews cannot keep pace with modern release cadences. Without automated security testing tools embedded in the pipeline, teams face a binary choice between speed and assurance.
4) Weak Testing Methods and False Positives
Poorly calibrated security tools generate high volumes of false positives. Development teams learn to ignore alerts, at which point real vulnerabilities start slipping through.
5) Toolchain Incompatibility
Smart security technologies that integrate cleanly into existing CI/CD workflows remain a gap for many enterprises. Retrofitting legacy toolchains is time consuming and often incomplete.
6) Delivery Speed as the Sole Priority
Focusing on fast paced delivery while pushing security and testing to a later stage is the single most common failure mode. A well designed CI/CD pipeline manages both delivery speed and security in parallel. The goal is not to slow down. It is to build security into the momentum.
Useful link: DevOps Configuration Management: A Guide to the Top Tools in the Field
The 4 Pillars of Effective Security Integration
Addressing these gaps requires a deliberate approach to security integration. 4 principles guide organizations that have made Secure DevOps work at enterprise scale.
1) Automate Security Processes
Integrating manual security tools into a fast moving CI/CD pipeline creates friction and slows delivery without improving coverage. Automation removes that friction. Automated security scanning, static analysis, dynamic analysis, and policy checks run continuously without adding time to the release cycle. This is not optional at scale. It is the baseline.
For teams exploring how cloud environments interact with automation, cloud security automation strategies and best practices offer a useful framework.
2) Integrate Security Across Every Pipeline Stage
Security integration means placing security controls at every stage of the pipeline, not just at designated review gates. Code commits trigger static analysis. Builds trigger dependency scanning. Deployments trigger configuration checks. Monitoring feeds threat intelligence back into planning. Each stage reinforces the one before it, and no stage creates an unguarded window.
3) Build Continuous Feedback Loops
A security control that is implemented once and never reviewed is a false assurance. Continuous feedback about implemented security features, their compatibility with new code, and their relevance to emerging threats keeps the security posture current. Feedback loops also enable teams to improve detection accuracy over time, reducing false positives that undermine developers’ trust in security tools.
4) Layer Multiple Security Processes
No single security solution covers the full threat surface of a modern enterprise application. Static analysis, dynamic analysis, software composition analysis, container security scanning, and infrastructure as code checks each address different risk vectors. Layering these processes ensures that a gap in one layer does not become an enterprise wide exposure.
Container security use cases that make Secure DevOps operational illustrate how layered security applies in containerized environments specifically.
6 Steps to Implementing Secure DevOps Successfully
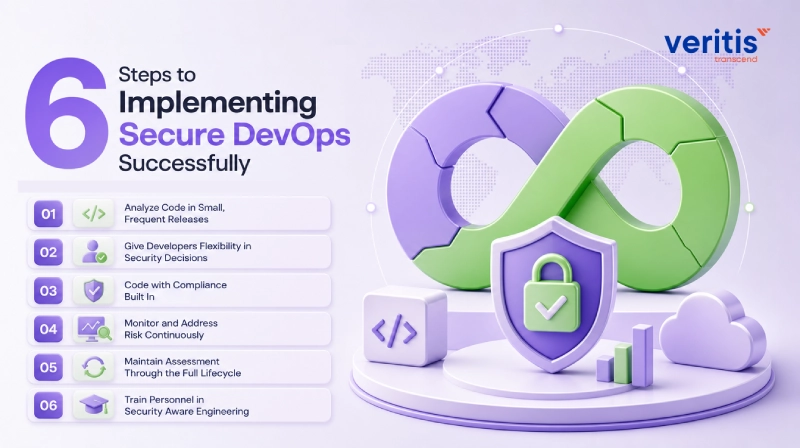
For enterprise teams ready to move from principle to execution, these 6 steps provide a structured path to implementation.
1) Analyze Code in Small, Frequent Releases
Breaking the code delivery process into small, frequent releases makes it substantially easier to identify and trace vulnerabilities. Smaller release units mean a smaller blast radius when an issue is found and a faster remediation cycle time.
2) Give Developers Flexibility in Security Decisions
Developers closest to the code have the best visibility into where security integration is needed and what form it should take. Empowering engineers to recommend and implement appropriate security controls, rather than waiting for a separate security team to review, shortens the feedback loop and improves coverage.
This principle is central to shift left DevOps, an approach that moves security and quality checks as early as possible in the development process.
3) Code with Compliance Built In
Compliance should not be a post delivery audit. When developers write code with the relevant compliance requirements in mind from the start, the organization maintains a continuous state of compliance across the process chain. This reduces audit preparation time and eliminates the scramble that accompanies late stage compliance checks.
4) Monitor and Address Risk Continuously
Vulnerabilities do not stop appearing after code is delivered. Continuous risk monitoring of newly deployed code allows early identification and resolution of issues before they propagate into dependent systems or reach end users.
5) Maintain Assessment Through the Full Lifecycle
Code revisits, periodic scans, and penetration tests should continue after initial delivery. The threat landscape evolves, and an application that was secure at launch may develop exposure over time as dependencies are updated, configurations drift, or new attack vectors emerge.
6) Train Personnel in Security Aware Engineering
Technology and process changes only hold if the people executing them have the right knowledge. Training engineers in security based coding practices and encouraging relevant certifications build organizational resilience that endures through tool changes and team transitions.
Building this kind of sustained capability is also what differentiates organizations with a genuine DevOps testing culture from those that treat quality and security as external functions.
Get Started with Secure DevOps Services
How Secure DevOps Compares to Traditional Security Models?
Understanding the structural differences between Secure DevOps and traditional security models helps leaders make the case internally for the required investment.
| Dimension | Traditional Model | Secure DevOps Model |
| Security timing | End of pipeline | Every pipeline stage |
| Security ownership | Dedicated security team | Shared across development and security |
| Testing frequency | Periodic | Continuous and automated |
| Compliance posture | Reactive, audit driven | Continuous and built in |
| Vulnerability discovery cost | High (production stage) | Low (development stage) |
| Release velocity impact | High friction | Low friction with right tooling |
The business case is straightforward. Catching a vulnerability in development costs a fraction of what it costs to remediate it in production, and the reputational and regulatory exposure of a production breach is rarely captured in any cost model.
Useful link: Building a High Performing DevOps Culture: Strategies and Best Practices for CEOs and CTOs
Secure DevOps in Practice: Real World Application in the Analytics Industry
A practical demonstration of what this looks like in production comes from Veritis’s engagement with a leading analytics service provider. The organization needed to streamline its deployment processes, improve cross team collaboration, and maintain rigorous security standards throughout a high velocity development lifecycle.
By embedding security integration across the CI/CD pipeline, standardizing automated testing, and aligning compliance checks with the release process, the team achieved measurable improvements in deployment frequency, vulnerability detection rates, and audit readiness. The engagement illustrates that Secure DevOps at enterprise scale is an executable model, not a theoretical one.
For organizations in other regulated or data intensive industries, how Veritis enabled secure cloud storage for a petcare enterprise demonstrates the same principles applied in a different vertical context.
Conclusion
Security integration is not a capability gap that more tooling automatically closes. It is a governance decision about where security accountability sits in the organization. Enterprises that have moved security ownership to the left, to the developers building the software, and have automated the enforcement of security policy across the pipeline, are the ones reporting measurable gains in both delivery speed and security posture.
The organizations still treating security as an audit function at the end of the pipeline are not behind on tools. They are behind on operating model design. That is a more expensive gap to close later than it is to address now.
Veritis brings the delivery experience, the toolchain expertise, and the security engineering depth to help enterprise teams close that gap without disrupting active development programs. If your DevOps program is outpacing your security posture, that is the conversation to have next.
Connect with a Veritis DevOps Security Expert to assess your current pipeline and define the right security integration roadmap for your environment.