Security debt is one of the most expensive liabilities on any enterprise technology balance sheet. Organizations that bolt security onto the end of the software development lifecycle spend, on average, 30 times as much fixing a defect found in production as they do fixing one caught during design. That single data point explains why the pros and cons of DevSecOps matter to every CTO, CIO, and CISO making decisions about pipeline architecture today.
This guide cuts through the noise. It explains what DevSecOps actually delivers, where it genuinely struggles, and how enterprise teams can position it for measurable success.
What is DevSecOps and Why Does It Matter Now?
DevSecOps brings security controls, testing, and accountability into every stage of the DevOps pipeline, making security a shared and continuous responsibility. The term fuses Development, Security, and Operations into a single, unified workflow covering every phase of the software development lifecycle (SDLC).
Where traditional models handed a finished product to a security team for review, DevSecOps services embed threat modeling, static analysis, dependency scanning, and compliance validation into each build, test, and release stage. Developers receive security feedback in the same sprint they write code, not weeks later when the context is gone, and the fix is exponentially more expensive.
According to GitLab’s 2021 Global DevSecOps Survey of nearly 4,300 professionals, 25% of respondents wanted complete test automation, and 60% of developers were releasing code at twice the speed compared to prior years. Those gains do not come without trade offs, which is precisely why understanding both sides of the ledger is essential before committing to a transformation program.
For a broader view of how DevSecOps fits within the larger DevOps evolution, see Pros and Cons of DevOps Methodology for Enterprises.
How DevSecOps Works: The Core Workflow
Understanding the workflow is a prerequisite for a fair evaluation of its advantages and disadvantages. The phases of DevSecOps follow a continuous loop:
1) Plan
Security requirements, threat models, and compliance constraints are defined alongside functional requirements. Engineers identify attack surfaces before a single line of code is written.
2) Develop
Developers write code within guardrails enforced by integrated security plugins. Code review procedures include a security lens by design.
3) Build
Source code compiles through automated toolchains that run static application security testing (SAST) on every commit.
4) Test
Automated pipelines execute dynamic application security testing (DAST), dependency scanning, and integration security tests in parallel with functional tests.
5) Deploy
Infrastructure as Code (IaC) tools automate environment provisioning with security configurations baked in. No manual, inconsistent setup.
6) Operate
Runtime monitoring and intrusion detection tools continuously monitor production. Operations teams perform periodic security maintenance as a standing discipline.
7) Scale
Governance frameworks ensure security controls grow with the system, preventing resource waste and configuration drift in large data environments.
The version control system underpins the entire chain. Every change is traceable, reviewable, and auditable, directly supporting compliance postures under frameworks such as SOC 2, HIPAA, and PCI DSS.
Useful link: DevSecOps Implemention : Enhancing Security for an Energy Services Firm
The Advantages of DevSecOps
1) Faster Delivery Without Sacrificing Security
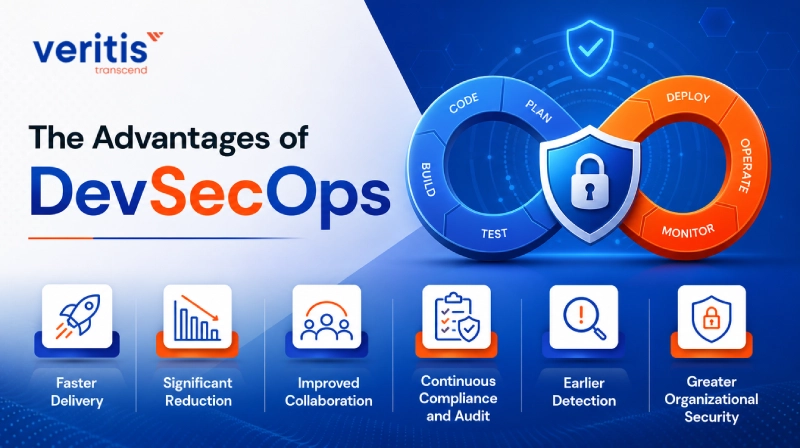
The most counterintuitive benefit of DevSecOps is that embedding security actually accelerates delivery. When security checks run automatically in the pipeline, they do not create a manual queue that stalls releases. Vulnerabilities surface in hours, not weeks. Development teams patch issues in the same sprint, keeping release cadence intact.
Veritis demonstrated this with a global telecom operator that needed to unify software delivery across mobile, broadband, video, and data services. By establishing a DevOps Center of Excellence and embedding automated CI/CD pipelines using Jenkins, Puppet, Ansible, and Infrastructure as Code, the organization achieved a 2x faster release cadence with predictable, repeatable deployments and a 60% reduction in manual effort and handoffs.
2) Significant Reduction in Remediation Cost
Finding a vulnerability during design costs a fraction as much as fixing it in production. DevSecOps shifts that discovery left. Automated SAST and DAST tools catch coding errors, insecure dependencies, and misconfigured components before they reach a live environment. For enterprises running dozens of simultaneous product lines, the cumulative cost avoidance is material and measurable.
3) Improved Collaboration Across Development, Security, and Operations
Siloed teams produce siloed risk. DevSecOps replaces the traditional handoff model with shared ownership. Developers understand the security implications of their code. Security engineers understand the delivery constraints developers operate under. Operations teams have visibility into both. That alignment shortens feedback loops, reduces blame cycles, and produces a higher quality product.
The DevSecOps best practices for security that drive this collaboration include shared dashboards, joint retrospectives, and security champions embedded within development squads.
4) Continuous Compliance and Audit Readiness
Compliance is a mandatory requirement across financial services, healthcare, and defense contracting. DevSecOps automates compliance checks against defined policy baselines, generating audit trails as a byproduct of normal operations. Security configurations are version controlled. Policy exceptions are logged. Evidence collection for audits becomes a report export rather than a weeks long manual exercise.
5) Earlier Detection of Vulnerabilities Reduces Production Risk
Runtime monitoring and automated scanning in DevSecOps pipelines mean that security posture is not a point in time snapshot. It is a continuous measurement. Teams detect anomalies, misconfigurations, and emerging threats in real time, significantly reducing the window of exposure between introduction and remediation. This is especially relevant for cloud security challenges, where misconfigured resources remain among the leading causes of breach.
6) Greater Organizational Security Maturity
DevSecOps is as much a cultural transformation as a technical one. When every engineer takes responsibility for security outcomes, the organization’s overall maturity rises. Security awareness becomes embedded in hiring, onboarding, and performance expectations. That maturity compounds over time, making the enterprise progressively harder to breach.
The Disadvantages of DevSecOps
A candid assessment of DevSecOps must acknowledge the genuine obstacles. Executives who proceed without understanding these risks tend to underinvest in the areas that determine whether the transformation succeeds or stalls.
1) Initial Speed Can Mask Early Vulnerabilities
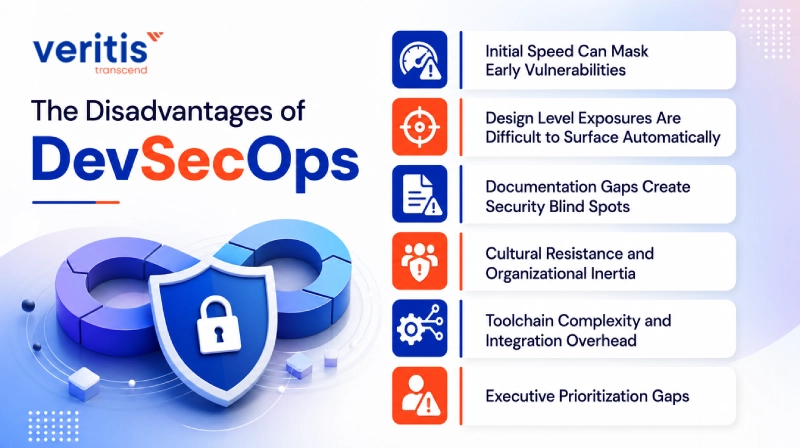
DevSecOps accelerates the early stages of development, and that velocity can, paradoxically, create risk. Teams moving quickly through design phases may skip rigorous threat modeling in favor of iteration speed. Automated tools efficiently catch known vulnerability patterns, but they are less effective at surfacing complex business logic flaws that require human review and domain knowledge. Discipline in the planning phase is non negotiable.
2) Design Level Exposures Are Difficult to Surface Automatically
The agile foundation of DevSecOps relies on client feedback and rapid iteration to shape the product. That model works well for functional requirements. It is less effective for architectural security design. Without structured threat modeling sessions early in every sprint cycle, design level exposures can accumulate across iterations, becoming expensive and architecturally complex to remediate later.
3) Documentation Gaps Create Security Blind Spots
Rapid iteration often deprioritizes documentation. For security teams joining a project midstream, sparse documentation means more time spent reverse engineering application logic before meaningful threat analysis can begin. Business logic vulnerabilities, in particular, require deep contextual understanding that documentation should provide but often does not in fast moving agile environments.
4) Cultural Resistance and Organizational Inertia
Not every engineering culture willingly embraces security accountability. Developers accustomed to passing security work downstream often resist the additional responsibility. Security teams that have historically operated as gatekeepers may struggle to adapt to an enabling, advisory role. Without active sponsorship from C-suite leadership, these cultural tensions undermine the transformation before tooling decisions ever matter.
5) Toolchain Complexity and Integration Overhead
A mature DevSecOps environment incorporates SAST, DAST, software composition analysis (SCA), secrets detection, container scanning, and infrastructure policy engines. Integrating, maintaining, and tuning these tools across complex enterprise environments requires specialized skills. The DevSecOps tools landscape is rich, but selecting and integrating the right combination demands expertise that many teams need to build or acquire.
6) Executive Prioritization Gaps
Security transformation requires budget, headcount, and tolerance for short term friction. When executive leadership does not prioritize security as a strategic business outcome, DevSecOps initiatives are underfunded, scope is trimmed, and security testing reverts to end of cycle reviews. The business case must be made in the language of risk and financial exposure, not tooling capability.
Schedule a DevSecOps Consultation
Pros and Cons of DevSecOps: Summary Comparison
| Dimension | Advantage | Disadvantage |
| Speed | Faster release cadence with security integrated | Initial velocity can obscure early design flaws |
| Cost | Lower remediation cost through shift left detection | Significant upfront toolchain and training investment |
| Compliance | Continuous audit readiness and automated evidence | Policy configuration requires ongoing maintenance |
| Culture | Shared security ownership across all teams | Resistance from teams accustomed to siloed roles |
| Risk | Continuous monitoring reduces production exposure | Business logic vulnerabilities still require human expertise |
| Tooling | Rich ecosystem of automation tools available | Integration complexity demands specialized skills |
Key Skills and Roles in a DevSecOps Team
The human dimension is where many DevSecOps programs underinvest. A capable DevSecOps engineer bridges three historically separate disciplines. The core competencies required include:
- Strong communication and collaboration skills to work across development, operations, and security functions
- Proficiency with DevOps toolchains including Ansible, Jenkins, GitHub, Docker, and container orchestration platforms
- Understanding of threat modeling frameworks, compliance requirements, and vulnerability classification
- Experience with automated code analysis, SAST, and DAST tooling to detect and remediate vulnerabilities at pace
- Familiarity with programming languages such as Java and Python to engage meaningfully in code reviews
- Knowledge of IaC platforms and deployment automation to enforce security at the infrastructure layer
Building this capability internally takes time. Many enterprises accelerate the journey by partnering with specialists who bring proven frameworks and toolchain experience to reduce ramp up time.
How to Maximize DevSecOps ROI: Strategic Considerations
1) Start With a Security Maturity Assessment
Before selecting tools or restructuring teams, establish a baseline. Understand where vulnerabilities currently enter the pipeline, how long they persist, and what remediation costs look like. That baseline makes the business case for investment and creates the measurement framework that proves ROI.
2) Secure Executive Sponsorship First
DevSecOps is a business transformation, not a technology project. It requires C-suite alignment on risk tolerance, budget authorization, and cultural expectations. Without that alignment, the program will stall when it encounters organizational resistance.
3) Invest in Training Before Tooling
Tools amplify capability. They do not create it. Engineers who do not understand the security risks they are scanning for will not act effectively on tool output. Security awareness training, threat modeling workshops, and cross functional exercises build the judgment that makes automation meaningful.
4) Adopt an Incremental Integration Approach
Replacing every security process simultaneously disrupts without proportional benefit. Identify the highest risk pipeline stages and integrate security controls there first. Expand coverage incrementally, measuring impact at each step. This approach demonstrates value quickly and builds organizational confidence in the model.
For organizations implementing continuous application security, this phased approach is often the difference between a successful program and a stalled pilot.
Useful link: All You Need to Know About DevSecOps and its Implementation
Case Study: Global Telecom Operator Accelerates Secure Delivery
A leading global telecom operator faced fragmented toolchains and manual processes that delayed releases and increased production risk. Security and compliance checks were reactive, leaving vulnerabilities to surface in production rather than during development.
Veritis established a centralized DevOps Center of Excellence to align development, operations, and security under a shared delivery framework. The team implemented automated CI/CD pipelines using Jenkins, Puppet, and Ansible, embedded early security and compliance scans into each build, and standardized toolchain integration across Bitbucket, Maven, JIRA, and Docker.
The results were measurable and rapid:
- 2x faster release cadence with predictable, repeatable deployments
- 60% reduction in manual effort and cross team handoffs
- Proactive security validation ensured continuous compliance and minimized production risk
This outcome reflects what DevSecOps delivers when executive sponsorship, toolchain investment, and cultural alignment are present simultaneously.
Read the complete case study: Telecom Multinational Company Embraces DevOps.
Strategic Insight: The Security Debt Question
Every quarter that an enterprise delays DevSecOps adoption is a quarter of accumulating security debt. That debt is not abstract. It manifests as longer incident response windows, higher breach remediation costs, failed compliance audits, and engineering time diverted from product development to emergency patching.
The pros and cons of DevSecOps are not equally weighted. The disadvantages are real but manageable with the right investment in skills, culture, and phased implementation. The advantages compound over time. The organizations ranking highest on software delivery performance metrics are, consistently, the ones that have made security a first class engineering discipline rather than an external control.
For enterprises ready to move from evaluation to execution, Veritis brings over a decade of delivery experience with Fortune 500 organizations and mid market leaders undergoing security and compliance transformation. Our approach begins with your specific risk profile, not a generic toolchain recommendation.
To begin building a program that delivers measurable outcomes from the first engagement.