Digital banking has made payments and account services easier to access, while expanding the channels criminals can target. Cybersecurity is therefore a business resilience priority: banks need to protect customer data and transactions while maintaining reliable services.
IBM’s 2026 Cost of a Data Breach Report puts the average cost of a financial services breach at $6.3 million globally. This is a study average, not a prediction of any individual bank’s losses.
What is Cybersecurity in Banking?
Cybersecurity in banking combines governance, people, processes, and technology to protect financial systems, customer information, and banking services from unauthorized access, disruption, and fraud. It covers digital channels, payment infrastructure, employee access, cloud platforms, core banking systems, and third party providers.
Banks must protect information from unauthorized disclosure and changes while keeping essential services available. Cybersecurity and fraud management also need to work together: a customer can authenticate successfully and still be deceived into authorizing a fraudulent payment.
The Rise of Digital Transactions
Digital payments, mobile banking, and online account services have changed how customers manage money. Each channel also creates security requirements for identity verification, transaction authorization, data protection, and service recovery.
Understanding the Cyber Threat Field
Banking threats include phishing and social engineering, malware and ransomware, account takeover, payment fraud, data breaches, service disruption, and attacks through third party providers. A successful incident can cause financial loss, interrupt services, expose customer information, and trigger regulatory or contractual obligations.
Useful Link: The Future of IT Financial Management: Trends and Innovations
Addressing Unique Challenges in Banking
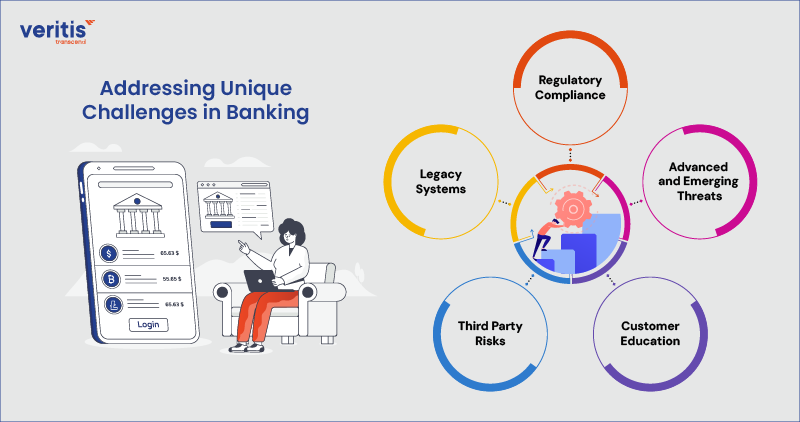
1) Regulatory Compliance
Requirements vary by jurisdiction, the services a bank provides, and the data it handles. Banks should map applicable privacy, security, payment card, and supervisory requirements to control owners and evidence.
For US banking organizations, a qualifying computer security incident must be reported to the primary federal regulator as soon as possible and no later than 36 hours after the organization determines that it has occurred. The EU’s Digital Operational Resilience Act (DORA) has applied to covered financial entities since January 17, 2025. Confirm applicability and reporting obligations with legal and compliance teams.
Veritis can help financial organizations align cybersecurity controls, monitoring, and reporting with applicable business and compliance requirements.
2) Legacy Systems
Numerous banks rely on outdated IT systems that may lack the essential security capabilities to withstand contemporary cyber threats. Prioritize unsupported software, exposed systems, privileged access, and dependencies tied to critical payment services. Modernization should include security requirements and operational recovery plans.
Veritis can support legacy modernization and digital transformation planning through its digital transformation services.
3) Third Party Risks
Banks often collaborate with third party vendors for various services, introducing additional cybersecurity risks in banking. Assess vendors before onboarding and throughout the relationship. Track the systems and data they can access, security obligations, incident notification terms, and exit or contingency plans.
Veritis can help organizations assess third party exposure and strengthen risk management processes.
4) Customer Education
Educating customers about cybersecurity best practices is one part of fraud prevention. Explain how customers can recognize suspicious requests, verify payment changes, and report suspected account compromise through trusted bank channels.
Veritis can support security awareness and training programs for employees and customers.
5) Advanced and Emerging Threats
Banks face changing threats, including AI enabled impersonation, evolving malware, and attacks against identities and digital services. Quantum risk calls for cryptographic inventory and longer term planning; it should be considered separately from active threats such as phishing and ransomware.
Veritis can help strengthen threat monitoring and security operations in line with an organization’s risk priorities.
Implementing Robust Security Measures in Banking
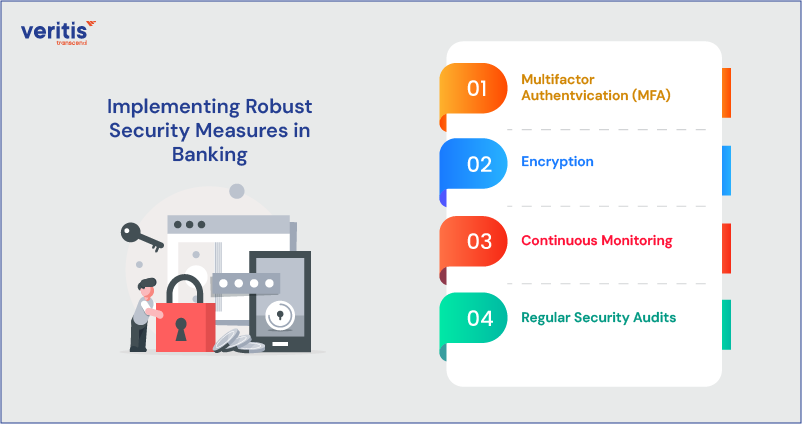
Banks can use the following measures to protect digital transactions and improve detection and response.
1) Multifactor Authentication (MFA)
Introducing Multi Factor Authentication (MFA) enhances cybersecurity in banking by mandating users to provide multiple verification methods before gaining access to their accounts. MFA can reduce unauthorized account access, but it does not prevent every scam or account takeover. Banks should prioritize phishing resistant authentication for high risk access and protect account recovery, session management, and payment approval workflows.
2) Encryption
Securing confidential data during transmission and while stored protects it from unauthorized access. Encryption should be supported by strong key management. Limit access to keys, protect secrets, and separate cryptographic administration from routine application access.
3) Continuous Monitoring
Financial institutions should utilize robust monitoring systems to identify and address threats promptly Correlate identity, application, network, and transaction signals so teams can investigate suspicious activity and respond before an incident spreads.
4) Regular Security Audits
Ongoing security evaluations and penetration tests play a key role in revealing vulnerabilities within banking networks. Track findings to remediation, prioritize exposed and critical systems, and test recovery procedures as part of the security program.
Useful Link: 8 Factors That Drive Digital Transformation in Banking Industry
How Does Cybersecurity in Banking Secure a Digital Transaction?
Security controls need to cover the full payment journey. A secure login alone does not confirm that a transaction is legitimate.
| Transaction stage | Core control | Business outcome |
| Customer signs in | Strong authentication, device checks, and secure recovery | Reduce unauthorized account access |
| Customer adds a beneficiary | Recipient validation and additional verification when risk increases | Reduce fraudulent payment redirection |
| Customer submits a payment | Authorization checks, transaction limits, and behavioral analysis | Identify suspicious instructions before execution |
| Systems exchange payment data | Encryption, API authorization, and integrity checks | Protect payment details between services |
| Payment completes | Audit logs, reconciliation, and customer notifications | Support detection, investigation, and dispute handling |
| An incident occurs | Containment, recovery testing, and escalation | Limit disruption and restore trusted operations |
Risk based controls can consider payment amount, recipient history, device behavior, session context, and unusual access patterns. Depending on risk, a bank may request additional verification, place a temporary hold, or refer a transaction for review.
Secure software delivery also matters. DevSecOps practices help teams identify application vulnerabilities and configuration problems before changes reach payment systems.
5 Most Common Digital Payment Risks
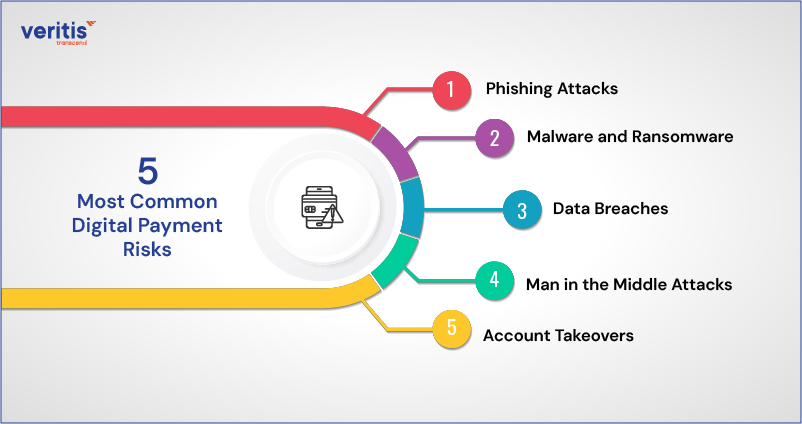
1) Phishing Attacks
Cybercriminals use deceptive emails, messages, or websites to trick users into revealing sensitive information, including credit card numbers, personal identification, login credentials, and other details.
2) Malware and Ransomware
Malware can compromise a user’s system, harvest sensitive financial data, undermine security, or hold data for ransom, leading to financial loss or identity theft.
3) Data Breaches
Unauthorized access to a company’s database or payment processing system can result in the theft of sensitive customer data, including credit card numbers, names, and addresses, leading to potential fraud and financial losses.
4) Man in the Middle Attacks
Hackers intercept communications between users and the payment gateway, allowing them to eavesdrop on sensitive information or modify transaction details, leading to unauthorized payments or identity theft.
5) Account Takeovers
Cybercriminals gain unauthorized entry into a user’s account through stolen credentials or brute force attacks, enabling fraudulent transactions or theft of personal information.
Banks should combine technical safeguards with customer guidance. Encourage customers to report suspicious requests through verified channels and monitor their accounts for unrecognized activity.
Useful Link: The Rise of Artificial Intelligence and Machine Learning in Financial Decision Making Processes
Use Cases for Cybersecurity in Action
1) Phishing Prevention with AI Powered Filters
Email and message filters can flag suspicious links, attachments, and sender behavior before messages reach customers or employees.
2) Real Time Transaction Monitoring
Transaction monitoring can flag unusual payment patterns for additional verification or investigation.
3) Endpoint Security and Zero Trust Adoption
Banks must secure every device to prevent attacks. Endpoint protection combined with Zero Trust reduces ransomware threats and insider breaches. This creates a stronger foundation for bank network security and data security in banking industry standards.
4) Secure Mobile Banking Applications
Mobile banking applications should protect sessions and sensitive data, and use strong authentication where appropriate.
5) Vendor Risk Management and Third Party Assurance
Maintain an inventory of provider access, assess security responsibilities, and plan for incidents or service outages involving critical vendors.
6) Incident Response and Resilience Planning
Define incident roles across security, fraud, payments, legal, communications, and executive leadership. Test containment, backup restoration, and transaction reconciliation.
7) Continuous Security Training and Culture Building
Give employees practical guidance on recognizing suspicious requests, reporting incidents, and handling sensitive information.
8) Cloud Security and Compliance in Banking
For cloud workloads, define shared security responsibilities, control access, protect data, monitor configurations, and test recovery. See 5 Key Benefits of Implementing Cloud Financial Services for Your Business.
Useful Link: 5 Key Benefits of Implementing Cloud Financial Services for Your Business
Benefits of Cybersecurity in Digital Banking
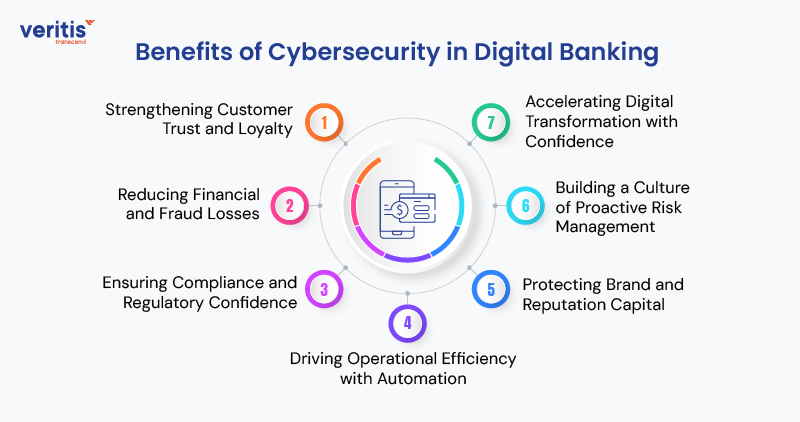
1) Strengthening Customer Trust and Loyalty
Robust cybersecurity in banking gives customers the confidence that their information and money are safe. Trust is the foundation of growth, and secure digital transactions reinforce loyalty while positioning the bank as a leader in the cybersecurity in banking industry.
2) Reducing Financial and Fraud Losses
Cyberattacks can erode profitability, but adequate safeguards prevent them from becoming business threats. Proactive measures reduce cybersecurity breaches in banking, protect against fraud, and secure shareholder value. Strong bank data security frameworks backed by advanced data security in banking industry practices build long term resilience.
3) Ensuring Compliance and Regulatory Confidence
Regulatory expectations continue to rise across global markets. Meeting and exceeding cybersecurity for banks requirements reduces the risk of penalties and strengthens confidence with regulators. Alignment with leading cybersecurity and financial services standards demonstrates accountability and sound governance.
4) Driving Operational Efficiency with Automation
Automated monitoring and real time detection improve efficiency while lowering costs. Streamlined operations strengthen cybersecurity in financial services and free resources for innovation and customer focused initiatives.
5) Protecting Brand and Reputation Capital
Reputation is one of the most valuable assets in banking. Preventing cybersecurity risks in banking ensures that institutions avoid headline grabbing breaches that undermine trust. Strong preventive measures maintain confidence among customers, investors, and regulators.
6) Building a Culture of Proactive Risk Management
Cybersecurity is not only about technology, it is about mindset. Ongoing awareness programs and leadership visibility strengthen bank network security and resilience. Institutions that embed security into culture minimize vulnerabilities and ensure continuity.
7) Accelerating Digital Transformation with Confidence
Innovation demands trust. With a strong cybersecurity foundation, banks can confidently expand fintech, cloud, and mobile services while protecting customer data. Embedding cybersecurity consulting services in finance ensures digital transformation happens securely and at scale.
A well governed cybersecurity program can help banks protect customer trust, reduce fraud exposure, improve service continuity, and support secure digital transformation. Outcomes depend on effective implementation, ongoing testing, and clear accountability.
Case Study: Building a Resilient Cybersecurity Framework in the Digital Services Sector
Veritis collaborated with a fitness and wellness platform to implement a comprehensive cybersecurity transformation. The goal was to protect sensitive user data and digital transactions. Veritis deployed encryption protocols, real time threat monitoring, access controls, and secure application practices to build a robust defense.
This cross industry example shows how security controls can be applied to a digital platform. It is not a banking implementation, and the available case details do not provide quantified results.
Read the Complete case study: Building a Resilient Cybersecurity Framework in the Digital Services Sector.
Conclusion
Banks can secure digital transactions by aligning identity controls, payment monitoring, infrastructure security, and incident recovery. The work starts with understanding the highest risk services and confirming that controls protect customers without interrupting legitimate payments.
Veritis helps organizations strengthen cybersecurity and modernize complex environments. Contact Veritis to discuss a banking cybersecurity assessment or improvement plan.