Traditional software delivery often treats quality and security as end of pipeline concerns, waiting until the final stages to test, scan, and validate code. Shift left DevOps (or DevOps shift left) overturns this model by embedding validation earlier in the development lifecycle.
This shift left methodology and shift left approach in DevOps answer the question, “what is shift left approach?” by moving automated tests and security checks into the design and requirements phases. By shifting left in DevOps and adopting a robust left shift strategy, teams drive shift left development, leveraging modern shift left technology to catch defects before they ever reach staging. Embracing DevSecOps shift left and a proactive shift left security DevOps stance ensures continuous compliance and quality.
- The shift left DevOps approach embeds testing, security (SAST, DAST, IAST, RASP), and compliance checks early in the CI/CD pipeline, delivering a cohesive shift left strategy that fortifies pipelines from commit through deployment.
- Early validation is core to shifting left in DevOps, provides faster feedback loops, boosts deployment frequency by up to 40%, and realizes 7–10× lower remediation costs, balancing speed with security.
- Core shift left methodologies, including automated unit/integration testing, dependency and container scanning, policy as code, and CSPM, operationalize your shift left approach in DevOps, accelerating delivery and minimizing risk.
- A phased roadmap (Assess, Plan, Pilot, Scale, Optimize) combined with standardized tooling and cross functional collaboration ensures successful shift left development and sustained innovation under a unified shift left security approach.
By partnering with Veritis, a proven leader in shift left DevOps transformation and DevOps consulting services, you gain experts in shift left technology who seamlessly integrate SAST, DAST, IAST, RASP, CSPM, and automated testing frameworks into your CI/CD pipelines. We guide you through every phase: Assess, Plan, Pilot, Scale, Optimize, to deliver rapid ROI, foster a culture of quality and security, and transform your delivery engine into a strategic growth driver with Veritis’ signature left shift strategy.
What is Shift Left DevOps?
Shift Left DevOps redefines traditional software delivery by integrating validation, testing, security scans, and compliance checks from the start of development. This methodology embeds automated quality gates into requirements gathering and design sessions.
- A shift left strategy integrates automated tests and security analyses into the initial development stages, detecting issues early to reduce rework and late stage schedule slips.
- DevSecOps shift left extends across the entire pipeline, from unit tests in developers’ IDEs to interactive security testing during feature branches.
This methodology fosters continuous inspection and strengthens quality, turning every commit into an opportunity to eliminate defects early.
Why is Shift Left Important in DevOps?
Shift Left is crucial because it reduces the cost and complexity of fixing defects by catching them early. It improves collaboration, integrates security into development, and speeds release cycles, ensuring software is secure and reliable from the start.
The Benefits of Shift Left DevOps
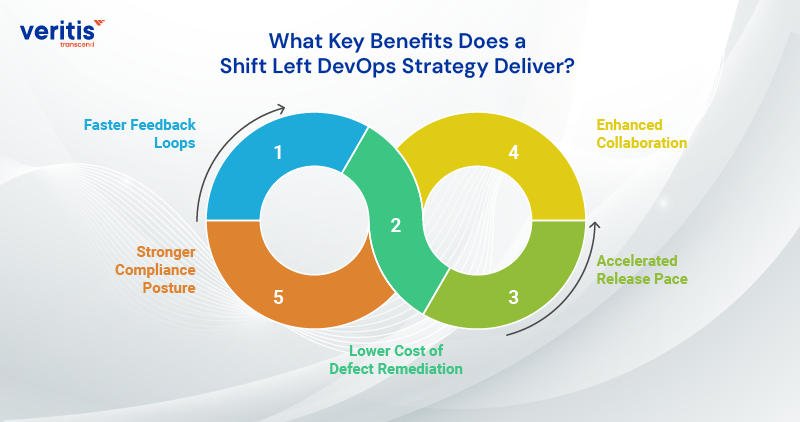
1) Faster Feedback Loops
By integrating automated tests, developers get real time insights, cutting bug fix cycles by up to 50%.
2) Lower Cost of Defect Remediation
Catching issues early is 7 to 10 times cheaper than fixing them after deployment.
3) Accelerated Release Pace
Increase deployment frequency by incorporating early validation, moving from 30% to as much as 60%.
4) Enhanced Collaboration
Breaking down silos through shared accountability fosters a culture of continuous improvement.
5) Stronger Compliance Posture
Policy as code ensures compliance is met at every pipeline stage, reducing audit preparation time.
Useful link: ITIL vs DevOps: Can Both Concepts Work Together?
What Phased Roadmap Drives Effective Shift Left DevOps Implementation?
| Phase | Activities | Success Metric |
| Assess | Inventory existing tools, baseline defect rates, and security posture. | Defect and vulnerability baseline |
| Plan | Define “shift left” policy scope; select SAST/DAST tools; train teams. | Policy catalog; toolchain readiness |
| Pilot | Onboard one critical service: integrate tests/scans into its CI pipelines. | % of pipelines shifted left |
| Scale | Roll out to all teams, enforce pass/fail gates, and monitor pipeline metrics. | Deployment frequency, failure rates |
| Optimize | Tweak rules to reduce false positives; automate remediation workflows. | Reduction in manual triage effort |
Shift Left DevOps Vs Shift Right DevOps
| Aspect | Shift Left DevOps | Shift Right DevOps |
| Timing of Validation | Early in development: unit tests, SAST, policy as code during shift left development, and CI builds. | Late/Production: user acceptance, synthetic monitoring, chaos engineering after deployment. |
| Primary Focus | Prevent defects and vulnerabilities through shift left security, DevOps, and automated pre commit gates. | Detect real world issues through logs, metrics, and real user monitoring. |
| Feedback Loop | Fast, in IDE and CI: immediate corrections during DevOps shift left cycles. | Slower, in staging/production: feedback after users interact with the system. |
| Cost Implications | Lower the cost of defect remediation by fixing bugs during code review rather than after release. | Higher operational costs and production remediation demands firefighting and hotfixes. |
| Tooling and Technology | Shift left technology: SAST, unit testing frameworks, policy as code tools. | Production observability: APM, logging platforms, chaos tools. |
| Security Posture | Proactive: Integrate security scans and threat modeling early (shift left security approach). | Reactive: incident response and patching after breach attempts. |
| Security Posture | Proactive: Integrate security scans and threat modeling early (shift left security approach). | Reactive: incident response and patching after breach attempts. |
| Team Collaboration | Requires cross functional collaboration from Day 0, aligning Dev, Sec, and Ops in a shift left methodology. | Emphasizes collaboration between DevOps and SRE during release and operations. |
| Quality Metrics | Code coverage, vulnerability counts, and build pass rates are key success metrics for a DevOps shift left strategy. | Uptime, MTTR, customer satisfaction, production error rates, and shift right effectiveness metrics. |
| Cultural Impact | Empowers developers with ownership of quality and security, reinforcing the DevOps shift left approach mindset. | Cultivates resilience and reliability focus, preparing teams to handle incidents gracefully. |
Useful link: MLOps vs DevOps: Which Drives Greater Business Impact for Your Enterprise?
The Benefits of Shift Right
1) Improved User Experience: By understanding how users interact with the software, teams can make adjustments that enhance usability.
2) Increased Reliability: Regular testing in a production environment helps ensure that the system can handle real world stresses and scenarios.
3) Continuous Feedback: Helps teams continuously improve and adapt their products based on user feedback and actual performance data.
Types of Shift Right Tests
- A/B Testing: Experimenting with features in production to measure user response.
- Dark Launching: Deploying new features to a subset of users to assess performance before full rollout.
- Chaos Engineering: Stress testing in production to ensure systems can withstand failures and outages.
Shift Right Tools
- Feature Flags: Allow teams to control the availability of features to end users without deploying new code.
- Real Time Monitoring: Tools like New Relic or Dynatrace provide insights into application performance and user interactions.
Shifting Security Left Through Collaboration
Incorporating security practices early in development fosters collaboration among development, security, and operations teams. This integrated approach strengthens security posture and reduces the risk of vulnerabilities being exploited.
How Can Shift Left DevOps Strengthen Security in Your Software Supply Chain?
Early detection and resolution of security vulnerabilities in your software supply chain protect against potential threats. By embedding security controls and compliance checks early in the DevOps pipeline, organizations can safeguard their applications efficiently.
Key Strategies:
- Integrate security tools into CI/CD: Leverage tools like SAST and DAST during code development to identify and fix vulnerabilities early.
- Enforce compliance and security policies: Ensure that every part of the supply chain complies with organizational standards.
The Role of Automation in Shift Left DevOps
Automation is crucial in Shift Left DevOps, enabling faster feedback loops and reducing manual errors. Automated testing and deployment tools streamline workflows and ensure consistent practices across development environments.
- Automated Testing: Implementing automated unit, integration, and acceptance tests at various stages of the pipeline.
- Continuous Integration/Deployment (CI/CD): Automated CI/CD pipelines reduce bottlenecks and enable rapid release cycles, making software delivery more efficient.
- Infrastructure as Code: Utilizing scripts to manage and configure infrastructure, maintaining consistency and reducing manual errors.
Conclusion
The shift left DevOps approach transforms delivery pipelines into proactive quality and security engines. By catching issues early, teams accelerate time to market, slash remediation costs, and foster a culture of shared responsibility. Organizations that embed shift left practices position themselves to deliver resilient, compliant software at scale and outpace their competitors in the digital era.
Next Steps:
- Map your current pipeline and identify the first candidate who represents the “left shift.”
- Pilot automated testing and security checks in a single service.
- Measure impact, refine your approach, and expand across the portfolio.
Embrace DevOps shift left with Veritis as your strategic partner. Our experts will tailor and implement the right tools, training, and dashboards to ensure your transformation delivers rapid ROI and sustainable innovation.
Deciding to adopt an approach is not a big deal, but making it succeed is what counts, and this is where Stevie Award winner Veritis comes in. Recognized for its DevOps excellence, Veritis, a leading DevOps consulting company, is the preferred choice of Fortune 500 companies and emerging organizations. We have developed cost effective solutions which don’t hamper quality or reliability. So reach out to us and embrace the best.