
Identity and access management (IAM) combines policies, processes, and technologies to manage digital identities and control access to systems and data. Identity management maintains user identities and their lifecycle information. Access management verifies users and applies policies to decide which resources and actions they are permitted to use.
The terms identity management, authentication, and access management are related, but they describe different functions. Authentication checks whether a user can prove a claimed identity. Authorization determines what that identity may access or do. IAM brings these controls together to help protect business systems and data.
Access management systems may be set up on-site, available by access asset managers under a cloud identity subscription model, or in a hybrid approach.
IAM typically includes:
- Identification of personnel
- Demarcation of roles to restrict unwarranted access
- Granting access permissions as and when required
- Management of permissions on an individual and group basis
- Ensuring protection for all the data and overall infrastructure
What is Identity Management?
Identity management creates and maintains digital identity records for employees, contractors, partners, service accounts, and other users or entities. These records may include attributes such as a person’s name, department, role, business unit, and employment status. Organizations use this information to manage accounts and assign appropriate access as responsibilities change.
Identity systems may support authentication through passwords, biometrics, security keys, or enrolled devices. These methods help verify a user, but they do not by themselves determine which data or systems that user is allowed to access.
Identity management also supports the user lifecycle: creating accounts when people join, updating identity information when their roles change, and disabling or removing accounts when they leave. Group and role assignments can simplify administration, but organizations still need to review permissions and remove access that is no longer required.
How Does Cloud Identity Management Works?
Creating and maintaining user roles and access rights is an organization’s primary focus of identity and access management. Identity and access solutions should provide a user repository, role definition and authorization engine, single sign on authentication system, password management, account provisioning, de provisioning, audit, and other features. An identity store or repository is the foundation of all IAM frameworks and solutions. The identity and access management services user repository might be a subsystem of a system like Active Directory, or it can exist independently as the only reliable source of information for all organization personnel. Then, roles and privileges will be assigned to users in the repository using the configuration of the role definition engine.
In practice, an organization’s identity repository may connect to human resources systems, directories, cloud platforms, and business applications. Provisioning and de provisioning workflows can then create, update, or disable accounts across connected systems. Organizations should also check that access changes have taken effect in those systems.
Single sign on (SSO) lets users authenticate through a central identity provider and access connected applications without signing in separately to each one. SSO simplifies sign in, but it does not automatically grant access to every application or resource. Each application must still enforce the user’s permissions. For example, a healthcare application must check that a signed in user is authorized to view the requested patient records.
Useful link: Key Business Benefits of Identity and Access Management
Why is IAM Important?
An identity management solution helps organizations keep accounts aligned with workforce changes and reduce unnecessary access. Automating onboarding, role changes, and offboarding can also reduce manual account administration and help prevent former employees or contractors from retaining access.
Without an effective cloud identity management system, tracking user information like email addresses may soon become a complicated problem. Identity management solutions help guard against security problems by enabling administrators to automate user account-related operations. This involves automated identity lifecycle management to allow workers access to the systems and apps they have been granted access to during onboarding.
By reducing time spent resolving user account issues, cloud identity management helps enterprises comply with sector-specific regulatory standards and save money. Moreover, when managing IDs, authentication, and authorization, identity and access management standardizes and even automates critical processes, saving time and money while lowering business risk.
IAM can help organizations apply consistent access policies, support security reviews, and maintain records of account and permission changes. Its effectiveness depends on accurate identity information, appropriately designed permissions, and enforcement across connected applications.
Understanding Access
Identification, authentication, and authorization are separate steps:
| Step | Question answered | Example |
| Identification | Which identity is being claimed? | An employee enters a corporate username. |
| Authentication | Can the requester prove control of an approved authenticator? | The employee signs in with an enrolled passkey or another approved method. |
| Authorization | Is this identity permitted to perform the requested action? | The finance application checks whether the employee may approve a payment. |
NIST’s Digital Identity Guidelines describe authentication as verifying that a claimant controls an authenticator associated with an account. Successful authentication is an input to an access decision; it does not, on its own, grant permission to view a document, change a setting, or approve a transaction.
What is Access Management?
Establishing an identity does not automatically mean a user can access a service. Access management evaluates an access request against the organization’s policies, which may consider the user’s role, permissions, requested resource, device, and other context. The system then allows, denies, or requests additional verification.
If a member of the accounting group logs into a system, they will have access to the company’s finances because they are part of that group. A person in engineering who gains access to the system can view engineering plans, charts, drawings, and documents that the accountant cannot see. Still, they will not be able to see the financial data.
Access management uses identity information to determine whether a request is authorized and enforces that decision through applications, gateways, or other controls. For example, an employee may be permitted to view a financial report but not edit it or approve a payment.
Common access management capabilities include SSO, multi factor authentication, federation, role based permissions, and policy enforcement. Authentication checks the user’s identity; authorization determines what that user may do.
Useful link: Best Practices for Effective IAM Implementation
What is the Difference Between Identity Management and Access Management?
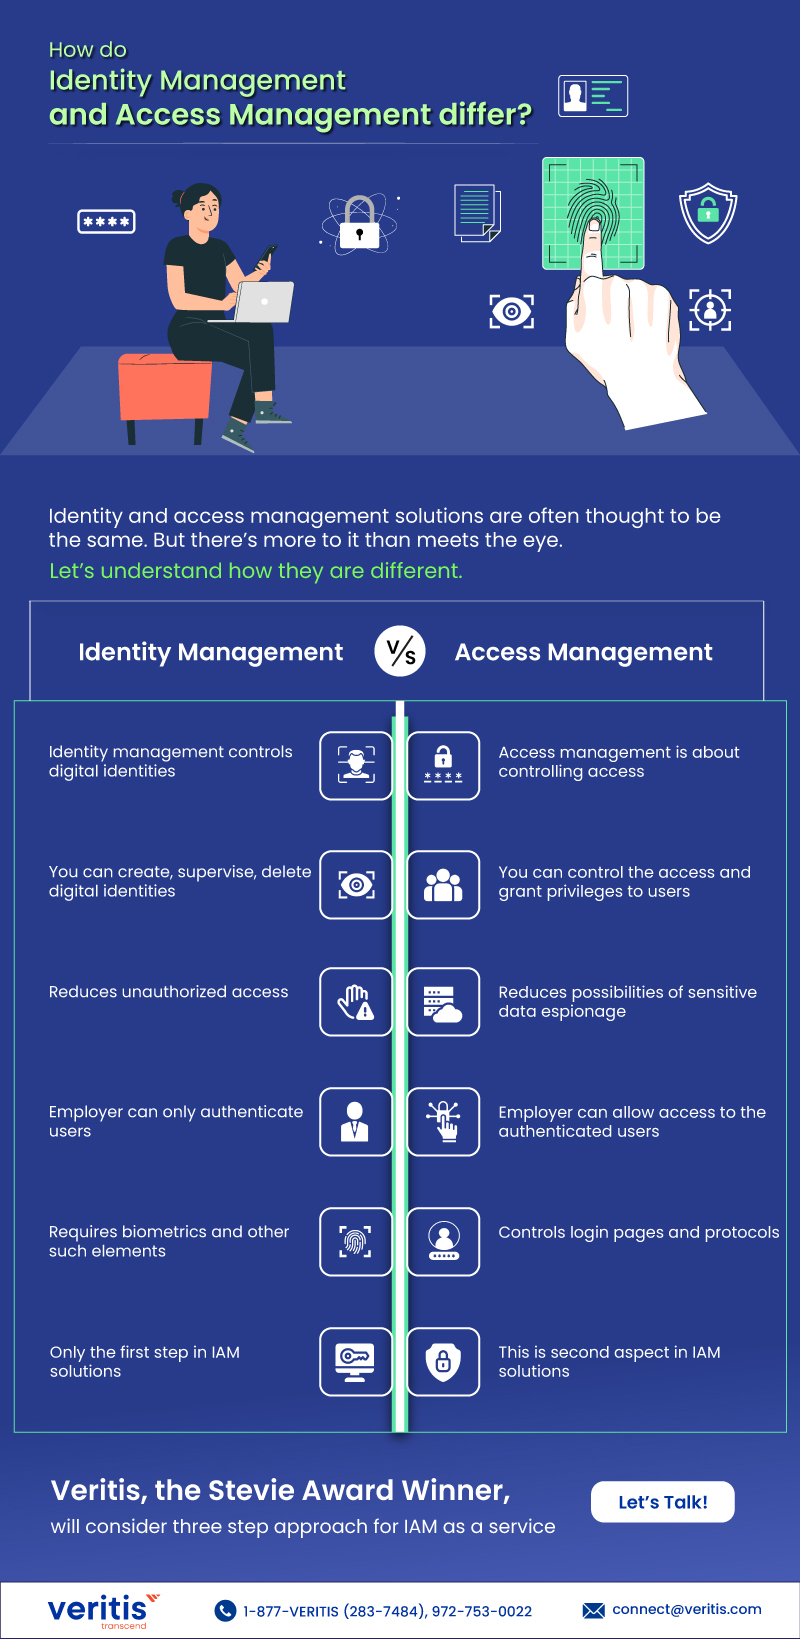
Identity management solutions, to put it simply, control digital identities. Digital qualities and database information are combined to form identities, which give each user a unique identity. Its administration entails creating, upkeep, supervising, and deleting such identities as they function within the corporate network. Businesses must ensure users have the right to do their tasks and minimize unauthorized access. Additionally, identity access management tools also manage authentication
Access management applies authentication and authorization policies to requests for applications, data, and other resources. It checks a user’s identity and determines whether the requested access is permitted.
In short, identity management maintains identity records and their lifecycle. Access management evaluates and enforces access requests using those identities and associated policies. Authentication and authorization are related steps, but they are not the same: authentication verifies a user, while authorization determines what the verified user may access.
Identity Management vs Access Management
| Dimension | Identity management | Access management |
| Primary question | Who is this identity, and is its information current? | What may this identity access or do? |
| Main responsibility | Maintain identities, attributes, accounts, and lifecycle status | Authenticate users and enforce access policies |
| Typical activity | Update an employee’s identity and accounts after a department transfer | Allow or deny access to a restricted application or action |
| Common risk | An account remains active after its owner leaves | A user can perform actions beyond their responsibilities |
Organizations need both functions. Accurate identity records cannot protect a resource if access policies are weak, and strong access policies cannot compensate for accounts that remain active after a person leaves.
Case Study: Enhancing Identity and Access Control with Azure AD Migration
Veritis assisted a global services firm in successfully migrating from SailPoint to Azure Active Directory (now Microsoft Entra ID), streamlining its identity and access management ecosystem. The objective was to modernize the organization’s identity infrastructure while ensuring secure, role based access across cloud and on prem environments.
This strategic migration enabled centralized identity management, improved authentication protocols, and simplified access governance, clearly distinguishing the roles of identity and access management in securing enterprise operations. The transition also enhanced IAM compliance, reduced overhead, and delivered a more seamless user experience.
Read the complete case study: Successful Migration of a Services Firm from SailPoint to Azure AD.
Microsoft Azure AD has been renamed Microsoft Entra ID. The case study describes this specific migration; the platforms’ capabilities should be assessed against the organization’s identity governance, provisioning, authentication, and access enforcement requirements.
How Do Identity Management and Access Management Work Together?
IAM connects identity lifecycle processes with authentication, authorization, and monitoring. For example, when an employee moves from procurement to finance, identity records and account assignments should be updated. Access policies then enforce the approved permissions when the employee requests financial systems or data.
Organizations should verify that changes reach connected applications and that obsolete permissions, sessions, and credentials are addressed. Disabling an account in a central directory may not remove access from an application that maintains separate accounts or active sessions.
Cloud environments require the same attention. AWS Identity and Access Management controls access to AWS resources. A user’s successful sign in does not automatically authorize every AWS action; cloud permissions must be deliberately assigned and reviewed.
Capping it Off
Identity management keeps user and account information current. Access management uses that information to enforce decisions about applications, data, and actions. Together, these capabilities help organizations manage access throughout the identity lifecycle.
Veritis provides identity and access management services to help organizations assess and strengthen IAM across their environments. Contact Veritis to discuss your identity and access management requirements.
Talk to an IAM consultant about validating those control paths across your enterprise environment.