Password related breaches, reset requests, and access delays create avoidable business risk. Passwordless authentication verifies identity without an account password, using methods such as passkeys, security keys, biometrics, authenticator apps, or temporary codes and links; its security depends on the method, enrollment, and recovery controls.
For enterprise leaders, the objective is not simply to remove a login field. It is to reduce exposure to stolen credentials while maintaining reliable access, clear accountability, and manageable operating costs. This guide explains how passwordless authentication works, where it improves security, and what an enterprise must address before deploying it at scale.
How do We Define Passwordless Authentication?
Passwordless authentication confirms a user’s identity without requiring an account password, helping enterprises reduce exposure to stolen credentials and password reset friction. Instead, users authenticate with a passkey, security key, certificate, authenticator app, or a temporary code or link delivered to their email address or mobile number.
In recent times, regular passwords have not been secure. Both remembering and resetting lost passwords are complex. Additionally, they are a primary target of cybercriminals: Verizon’s Data Breach Investigations Report found that 81% of hacking related breaches leveraged stolen or weak passwords.
That historical finding concerns a specific category of breaches, not all breaches or a current annual rate. Although the capabilities of passwordless authentication solutions differ, they all allow individuals to log into the account without creating a static password for that login method. Therefore, there is a chance you would improve security and user experience by removing passwords from the login process and going passwordless.
Passwordless authentication can benefit different sectors and use cases. For instance, businesses can provide physical security keys to authenticate staff members and control access to internal resources. Customers can confirm a transaction on their mobile devices using their fingerprints. Users who have forgotten their passwords may use a link in an email to log in.
However, passwordless authentication solutions aren’t restricted to these techniques or use cases. Instead, it has various implementations with different feature sets and advantages, all of which dwarf the built-in vulnerabilities of passwords.
What is the Problem With Passwords?
Passwords create risk because they are reusable secrets that users must protect and applications must verify. A stolen password can be used by someone other than its legitimate owner unless another control blocks access.
Several problems make passwords difficult to manage across an enterprise:
- Credential reuse: Employees and customers may reuse passwords across services. A breach elsewhere can then expose a business account through credential stuffing.
- Phishing: An attacker can create a convincing login page that collects a password and, in some cases, a temporary verification code.
- Operational friction: Forgotten passwords, expired credentials, and account lockouts generate support work and interrupt productive access.
- Recovery exposure: Help desk procedures, recovery email accounts, and identity verification exceptions can become routes into protected systems.
- Uneven application controls: Password policies, authentication protocols, and monitoring may differ between modern platforms and legacy systems.
Password managers, strong unique passwords, rate limiting, and MFA remain useful where passwords are still required. Passwordless authentication addresses a different issue: it can remove the reusable account secret from the supported login path rather than ask users to manage that secret more carefully.
The business case should therefore distinguish security improvement from convenience improvement. Removing password entry may improve usability, but an email link that an attacker can steal does not provide the same protection as a passkey bound to the legitimate service.
How Does Passwordless Authentication Work?
Passwords are replaced by alternative authentication variables, which are inherently safer in passwordless authentication. During password-based authentication, a user-provided password is compared to what is kept in the database.
In some passwordless systems, such as biometrics, a user’s unique characteristics are compared to passwords, and the comparison process is similar in both cases. For instance, a system can capture a user’s face, extract numerical information from it, and then compare it to verify information stored in the database.
In other passwordless systems, comparisons may take place in different ways. For instance, a system can send an SMS to a user’s mobile device containing a one-time passcode. The system then matches the user-entered passcode to the previous one.
Cryptographic passwordless authentication uses public and private key pairs, a principle also used in digital certificates. The private key creates a digital signature, and the public key lets the application verify it. This is different from delivering a temporary code through email or SMS, which does not necessarily use a public key credential to authenticate the user.
Passwordless authentication follows the same principles as digital certificates; cryptographic key pairs containing private and public keys are the foundations of passwordless authentication. Although both are referred to as “keys,” the private key is the actual key that unlocks the padlock, while the public key serves as the lock.
Regarding the operation of digital certificates, there is only one padlock for each key and vice versa. A user uses a tool (a mobile app, a browser extension, etc.) to produce a public private key pair to create a secure account. The private key is kept on the user’s local device and can only be accessed using a security measure like a fingerprint, PIN, or OTP. The user’s system wants a secure account and is given the public key.
Useful link: Security Breaches Rising Exponentially; Weak Authentications Exploited
What Happens During a Typical Passkey Sign In?
A passkey sign in usually follows these steps:
1) The user opens the legitimate application and selects a passkey sign in option.
2) The application sends a fresh cryptographic challenge through the browser or supported client.
3) The user authorizes the authenticator with a local biometric or PIN, as required by the configuration.
4) The authenticator signs the challenge using the private key associated with that service.
5) The application verifies the signature and checks relevant authentication requirements.
6) The identity platform applies access policies before establishing the session.
Authentication proves the identity claim; authorization determines what that identity can access. A successful passkey sign in does not replace entitlement controls, application permissions, or session monitoring.
Is Passwordless Authentication Secure?
Passwordless authentication can be secure, but its protection depends on the credential, delivery channel, enrollment process, and recovery controls. Phishing resistant methods such as passkeys, FIDO2 security keys, and appropriately configured certificate based authentication provide stronger protection against credential phishing than email links or SMS codes.
If you consider ‘safe’ synonymous with ‘unbreakable,’ then the answer is no. Not a single authentication method is impenetrable. While there may not be an obvious way to hack it, the most skilled hackers can find a way to get past its safeguards.
Passwordless methods remove some password related attack paths, but they are not uniformly more secure than every password based configuration. A dictionary attack, frequently regarded as a basic hacking method, is one example of how a bad actor may compromise a password based system by trying different passwords until a match is found. Cryptographic passwordless credentials remove the reusable account password that this attack targets.
A dictionary attack is possible even for amateur hackers. However, compromising a passwordless account does not always require sophisticated biometric spoofing. Attackers may instead target email accounts, mobile numbers, push approvals, account recovery, or an already authenticated session. Biometric systems can also face presentation attacks, making sensor quality and liveness detection relevant controls.
The practical security distinction is whether an attacker can capture or relay the authentication proof to another site:
- Passkeys and FIDO2 security keys: Bind authentication to the legitimate service, making them phishing resistant when implemented correctly.
- Certificate based authentication: Can provide phishing resistance when the protocol, private key protection, and certificate validation are configured appropriately.
- Email links and SMS codes: Can remove password entry, but remain exposed to compromised inboxes, number takeover, phishing, or real time relay.
- Push approvals: Depend on the authentication design. A simple approval prompt can be vulnerable to approval fatigue and social engineering; stronger cryptographic implementations offer different protections.
Passwordless authentication and multifactor authentication describe different properties. Passwordless means the login does not require an account password. Multifactor authentication requires distinct factor types. A security key or device credential combined with local biometric or PIN verification can satisfy multifactor requirements in supported configurations, while an email link alone does not automatically do so.
For enterprise security leaders, the weakest permitted route matters as much as the preferred login method. A phishing resistant sign in can be undermined if an attacker can bypass it through a weaker recovery process or password fallback. Access policy, help desk verification, session controls, and credential revocation must therefore be assessed alongside the authenticator.
Passwordless Connection vs Passwordless Login
A passwordless connection is a different kind of link distinct from any company, social, or existing database connection. Although users or social providers may have the same email address, their passwordless connection’s identity is different.
Account linking can connect a passwordless login identity with identities from other connections, just like linking multiple email addresses or mobile phone numbers used for the Passwordless connection.
How Can I Use Passwordless Authentication?
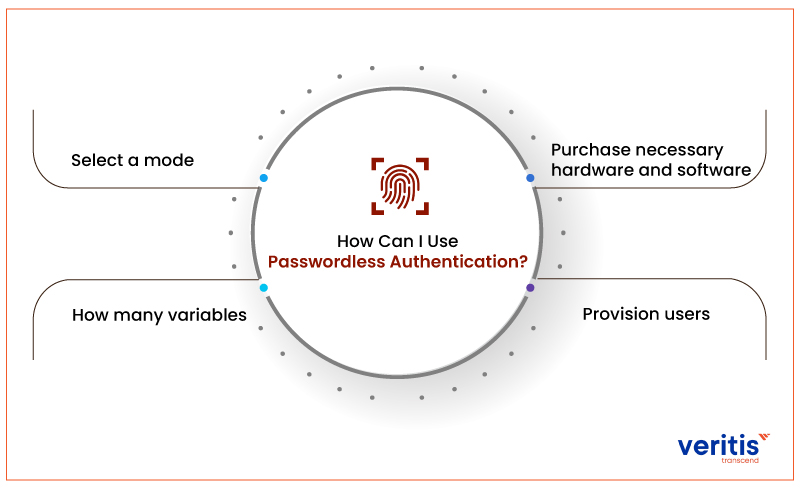
Here’s a strategy for adopting passwordless authentication into practice:
1) Select a Mode
The first step is to decide which authentication factor you desire. Options include hardware tokens, fingerprints, retinal scans, and magic linkages.
For enterprise access, prioritize phishing resistant methods such as passkeys, FIDO2 security keys, or appropriately configured certificates. Assess workforce, customer, privileged, and shared workstation access separately. The appropriate method depends on the application, device ownership, user population, and assurance requirements.
2) How many Variables?
It is recommended to use multiple authentication factors, regardless of whether you use passwordless authentication. Relying solely on one aspect is not advised, no matter how secure it seems.
Evaluate whether the chosen authenticator proves possession and requires local user verification. A biometric or PIN that unlocks a credential is different from an account password submitted to a server. Define additional controls for privileged access, sensitive transactions, unmanaged devices, and suspicious sign in activity.
3) Purchase Necessary Hardware and Software
You might need tools to establish biometric-based passwordless authentication. In addition, you might need to purchase software for other options, such as magic links or mobile OTPs.
Inventory existing identity providers, operating systems, browsers, managed devices, and application authentication protocols before purchasing new tools. Some environments can use existing platform authenticators, while others need security keys or certificate infrastructure. Validate compatibility with remote access, shared devices, and legacy applications rather than assuming a single method will cover every system.
4) Provision Users
Start adding users to your authentication system.
Establish a trusted enrollment process before issuing credentials. Pilot with representative users, including remote employees, contractors, administrators, and employees without suitable personal devices. Provide clear onboarding instructions and accessible alternatives, then define what happens when a device is lost, replaced, or unavailable.
Implementing passwordless authentication internally can take more time and effort. Therefore, many enterprises prefer to outsource their IAM needs. This expedites the procedure and lowers maintenance expenses and concerns.
What Should an Enterprise Pilot Include?
A useful pilot tests real business access rather than a demonstration login. Include users with different devices, accessibility requirements, working locations, and application dependencies.
Before expanding the rollout, validate:
- Enrollment from approved and unapproved devices.
- Access to business critical applications, remote access services, and administrative tools.
- Recovery after losing a phone, replacing a laptop, or damaging a security key.
- Employee termination and immediate credential revocation.
- Support escalation when the identity platform or delivery channel is unavailable.
- Access restrictions for contractors, shared workstations, and privileged accounts.
- Audit records that identify which authentication method was actually used.
Application changes should follow established testing and release controls. Where developers implement WebAuthn or change session handling, include authentication tests in the relevant phases of DevSecOps rather than treating identity integration as a separate deployment task.
Types of Passwordless Authentication
In the case of traditional username and password authentication, users must enter something they are aware of (a password) to prove their identity.
However, password-less authentication approaches call for the user to show that they are something (an inherent factor) or possess something (a possession factor), both of which are more difficult to defeat.
An important distinction is that a biometric may unlock a credential rather than authenticate directly to an application. Passkeys, for example, combine a cryptographic credential with local authorization through a biometric or PIN. FIDO2 security keys can hold these credentials on a separate physical authenticator. Windows Hello can use a device held credential unlocked locally, while certificate based methods authenticate through a certificate and its corresponding private key.
The methods below also overlap. Magic links are commonly email based, while OTPs can be delivered by email or SMS. These labels describe both authentication mechanisms and delivery channels, so they should not be treated as equivalent security categories.
| Method | What establishes access | Principal enterprise consideration |
| Passkeys and FIDO2 security keys | A signed challenge verified with a registered public key | Credential lifecycle, application support, and device bound versus synced credentials |
| Certificate based authentication | Proof of possession of a private key associated with a trusted certificate | Certificate issuance, renewal, revocation, and protocol configuration |
| Biometrics | A match to an enrolled biometric template, often authorizing a local credential | Sensor quality, accessibility, privacy, and fallback controls |
| Push notifications | Approval or cryptographic authorization through an enrolled app | Whether the implementation resists phishing and approval fatigue |
| Email links and email codes | Access to the registered mailbox and a valid temporary token | Mailbox compromise, phishing, and token handling |
| SMS codes | Access to the registered number and a valid temporary code | Number takeover, interception, and recovery exposure |
The most popular techniques for confirming both inherence and possession aspects are listed below:
1) Biometrics
Many physical characteristics are distinctive to each person. Without demanding an account password, biometric authentication employs these physical characteristics to help confirm identity. Facial recognition, for example, compares captured facial features with an enrolled template. Its accuracy depends on the system, operating conditions, and matching thresholds; there is no universal probability of uniqueness that establishes authentication security.
Examples of Biometric
- Fingerprint Scan
- Voiceprint
- EKG
- Facial Recognition
- Retinal Scan
2) Push Notifications
Users receive a push notification from an enrolled authenticator app on their mobile device and open the app to approve or authorize a sign in. The app’s capabilities determine whether this is an approval based workflow or a cryptographic passwordless authentication process. Authenticator apps are not interchangeable, and not every app supports push authentication.
Examples of Push Notifications
- Hardware token
- Authentication app
- Smart card
- Mobile device
3) Magic Links
In this type of password-less authentication, the login box prompts the user to input their email address rather than a password. They are then provided a URL in an email that they can use to log in. This procedure is repeated every time a user logs in.
Examples of Magic Links
- Accessing a Medium account
- Accessing a new Slack instance
4) One Time Passwords and Codes
In contrast to magic links, one-time passwords (OTPs) or one-time codes (OTCs) require users to enter a code that is sent to them (by email or SMS to their mobile device). Then, when a user logs in, this process is repeated.
5) Email Based Authentication
This type of password-less authentication encourages users to input their email addresses in the login boxes rather than asking for passwords. After that, they get an email with a link to a login page.
6) SMS Based Authentication
An individual first provides his phone number before a username and password. After entering their mobile number, the customer will receive a one-time-use code through SMS. The user will have access to his application after entering the one-time-use code in the login box.
7) Link Based Authentication
Link based authentication sends a temporary sign in URL through an approved channel, commonly email. The user follows the link rather than entering an account password. This overlaps with magic links; receiving an SMS code and typing it into a login box is code based authentication, not link based authentication.
Should Enterprises Choose Device Bound or Synced Passkeys?
Device bound passkeys remain with a specific authenticator. Synced passkeys can become available on additional devices through the credential provider’s synchronization and recovery mechanisms.
Neither model should be selected on convenience alone. Enterprises should evaluate who controls the credential provider account, which devices can receive credentials, how recovery works, and what happens when an employee leaves.
| Decision area | Device bound passkeys | Synced passkeys |
| Credential location | Restricted to a particular authenticator | Available across supported devices through a provider |
| Device replacement | May require another enrolled authenticator or trusted recovery | May support continuity through provider synchronization |
| Enterprise governance | Focuses on authenticator issuance, inventory, and revocation | Also requires assessment of provider accounts and synchronization controls |
| Access continuity | Depends on spare authenticators and recovery readiness | Depends on provider availability, account access, and supported devices |
| Selection criteria | Credential custody and controlled device access | Usability, portability, and acceptable provider governance |
Privileged access may warrant a different credential policy from general workforce access. Define those requirements explicitly rather than assuming every passwordless method offers the same assurance.
How Does Passwordless Authentication Fit With SSO and MFA?
Passwordless authentication, single sign on, and multifactor authentication solve different problems. Passwordless changes how identity is verified, SSO reduces repeated logins across applications, and MFA requires more than one factor type.
| Capability | Primary purpose | What it does not guarantee |
| Passwordless authentication | Remove the account password from a login method | Phishing resistance or multiple factors in every implementation |
| Single sign on | Reuse an authenticated identity across connected applications | A strong initial authentication method |
| Multifactor authentication | Require distinct factor types | Removal of passwords or resistance to real time phishing |
| Adaptive MFA | Adjust authentication requirements based on context and policy | Safe access without sound signals, enrollment, and recovery controls |
How Does Passwordless Authentication Support Zero Trust?
Passwordless authentication supports Zero Trust by strengthening identity verification at the access boundary. It does not establish Zero Trust on its own, because access decisions must also consider device health, least privilege, resource sensitivity, and ongoing session risk.
Zero Trust starts with secure access, but it continues after authentication. A user who has successfully presented a passkey should receive only the permissions needed for the task, not broad access because the credential is strong.
A practical architecture combines:
- Verified identity: Require an authentication method appropriate to the resource and user role.
- Device assurance: Check whether the endpoint meets management and security requirements.
- Least privilege: Limit entitlements and separate ordinary work from administrative access.
- Contextual policy: Evaluate relevant risk signals before allowing sensitive actions.
- Session controls: Monitor, restrict, or revoke access when circumstances change.
- Lifecycle governance: Remove credentials and permissions promptly when employment or responsibilities change.
The same principles matter for cloud workloads and deployment platforms. Passwordless workforce access should complement, rather than substitute for, the workload identity and secrets controls addressed in DevSecOps solutions for cloud security.
Human passwordless authentication also does not automatically solve machine identity. Service accounts, automation, APIs, and workloads require their own credential and authorization strategy.
Useful link: What is Operational Security (OPSEC) and How Does it Protect Critical Data?
Advantages of Passwordless Authentication
Passwordless authentication can improve access security, user experience, and operational efficiency when the chosen methods fit the environment. These benefits should be evaluated against an enterprise baseline rather than assumed from enrollment totals.
1) How Does Passwordless Authentication Enhance User Experience?
Passwordless authentication can reduce the need to remember passwords, manage expiration prompts, and recover forgotten account secrets. A supported passkey sign in can allow users to authorize access through a familiar local biometric or PIN.
The experience is most effective when employees understand which authenticator to use and can access their applications consistently. Fragmented enrollment instructions or frequent switches between passwords, codes, and security keys can limit the benefit.
Customer access presents a similar opportunity, but the business must test browser support, device changes, account recovery, and accessibility. Faster routine sign in is useful only if users can still regain access safely when circumstances change.
2) How Can Passwordless Authentication Create a Strong Cybersecurity Posture?
Phishing resistant passwordless methods reduce exposure to attacks that depend on collecting and reusing an account password. Passkeys also avoid placing a reusable private authentication secret on the application’s server.
This changes the attacker’s options, but it does not remove every attack path. A stronger cybersecurity posture requires protected enrollment, secure endpoints, constrained recovery, and appropriate access policies alongside the credential.
Enterprise leaders should define which risks the deployment is intended to reduce. A project designed to address credential phishing should require phishing resistant methods, not merely any login experience without a password field.
3) Can Passwordless Authentication Reduce Long Term Costs?
Passwordless authentication can reduce some password reset and account lockout work. Whether it lowers total operating costs depends on hardware, licensing, integration, support, and recovery requirements.
An assigned laptop with an existing platform authenticator may have a different cost profile from a workforce that needs issued security keys and replacements. Certificate based authentication may also require infrastructure and operational expertise that other approaches do not.
Build the financial assessment around actual support effort and deployment costs. Include enrollment assistance, spare authenticators, lost device recovery, application changes, administrator training, and ongoing lifecycle management.
4) How Can Passwordless Authentication Improve Productivity and User Experience?
Reliable passwordless access can reduce interruptions caused by forgotten credentials and repeated authentication tasks. Combining a suitable passwordless method with SSO can extend that improvement across connected applications.
Productivity gains should be measured in the work context. Examine login completion, failed access attempts, time spent resolving authentication problems, and interruptions to business critical workflows.
Frontline users, remote employees, and privileged administrators may need different access designs. Consistency means applying a clear policy to each group, not forcing every person to use the same device or interaction.
5) How Does Passwordless Authentication Reinforce Security?
Passwordless authentication reinforces security when access policy requires the intended credential and removes weaker routes that could bypass it. Revocation, recovery verification, and session controls determine whether the benefit persists after rollout.
For example, issuing security keys to administrators provides limited protection if those same administrators can recover access through an unverified phone call. The recovery route must meet the risk level of the account it restores.
Clear audit evidence is also important. Security teams should be able to determine which method was used, whether the required authentication strength was satisfied, and which policy allowed access.
These disadvantages do not make passwordless unsuitable. They identify the conditions that an enterprise must address to achieve dependable results.
1) Why Might Passwordless Authentication Have Higher Prices?
Some deployments require new security keys, upgraded devices, additional licenses, or certificate infrastructure. Integration work can also increase costs when applications do not support modern identity protocols or the selected authenticator.
The price of an authenticator is only one part of the investment. Budget for enrollment, procurement, distribution, replacement, support documentation, and incident procedures.
Existing capabilities may reduce new spending, but they still require assessment and configuration. A business case should compare the proposed deployment with the current operating baseline instead of assuming that removing passwords immediately creates savings.
2) Why Can Passwordless Authentication Be Difficult to Troubleshoot?
Passwordless access can depend on several components: the authenticator, operating system, browser, identity provider, application integration, and access policy. A failed sign in may originate in any of these layers.
Support teams need diagnostic procedures that distinguish credential problems from device compliance failures, policy blocks, expired certificates, and application session issues. Repeatedly asking a user to reenroll can create unnecessary disruption if the actual cause is elsewhere.
Define support ownership before launch. Help desk staff should know which logs to review, when to escalate, and how to restore access without bypassing identity verification.
What Passwordless Authentication Challenges Should Enterprises Plan For?
The principal challenges are security limitations, deployment cost and effort, and user acceptance. Each requires a specific implementation response rather than a general assurance that passwordless access is more secure or easier.
1) What Security Limitations Must Be Addressed?
The most important limitation is that passwordless methods have different assurance levels. Email codes, SMS codes, push approvals, passkeys, and certificates should not be placed in one undifferentiated security category.
Assess the complete identity lifecycle:
- Enrollment: How is identity verified before a new credential is registered?
- Credential protection: Where does the private key reside, and who can authorize its use?
- Recovery: Can an attacker exploit a weaker process to register a replacement?
- Revocation: How quickly can access be removed after device loss or employee departure?
- Sessions: Can existing sessions remain active after a credential is revoked?
- Fallback: Which users can still use passwords or lower assurance methods?
Regulated environments should map the selected configuration to applicable requirements. The label “passwordless” is not itself evidence of compliance, and biometric use may introduce privacy and accessibility considerations that require review.
2) How Should Enterprises Manage Deployment Cost and Effort?
Start with application and identity architecture, not procurement. An inventory reveals which systems can use centralized authentication, which need integration work, and which retain a separate password dependency.
Group applications by business importance, access pattern, and compatibility. Then sequence deployment so the organization can learn from a controlled pilot before expanding to more demanding workflows.
For custom applications, identity requirements should be considered alongside the business process changes involved in ServiceNow custom applications and other enterprise platforms. Registration, entitlements, recovery, and session behavior should be designed together rather than added after the application is complete.
Legacy systems may need federation, an access gateway, application modernization, or a temporary exception. Document which approach is being used and the residual risk. Do not report an application as passwordless if users still rely on a separate password route to reach it.
3) How Can Enterprises Improve Users’ Acceptance of Passwordless Authentication?
Users are more likely to adopt a new login method when they understand what will change and what will happen if their device is unavailable. Training should explain the actual sign in flow, unexpected prompts, recovery options, and support contacts.
Address practical concerns directly. Employees may not want to use personal phones for work, may lack a compatible device, or may be unable to use a particular biometric. An approved alternative prevents these constraints from becoming informal security exceptions.
Use pilot feedback to identify confusing language, unnecessary prompts, and difficult recovery steps. Adoption is a product of reliable access and clear procedures, not a communication campaign.
How Should Enterprises Measure Passwordless Authentication Results?
A passwordless program should report security coverage, user adoption, reliability, and cost. Enrollment alone does not show that users have stopped using passwords or that sensitive applications require phishing resistant access.
| Metric | What to measure | Why it matters |
| Passwordless login share | Eligible sign ins completed without an account password | Shows actual use rather than registrations |
| Phishing resistant coverage | In scope applications and accounts protected by required phishing resistant methods | Distinguishes stronger assurance from convenience only methods |
| Password fallback use | Sign ins through remaining password routes | Identifies continued dependency and potential bypasses |
| Authentication success | Successful and failed attempts by method and user group | Reveals reliability and configuration issues |
| Recovery volume | Requests by cause, resolution time, and verification route | Exposes usability problems and recovery risk |
| Support effort | Time and cost associated with authentication tickets | Supports an evidence based operating cost assessment |
| Credential revocation time | Time from a loss or departure event to effective access removal | Measures lifecycle responsiveness |
| Application coverage | Applications integrated, pending, or excluded | Makes modernization gaps visible |
Establish a baseline before deployment and compare results over consistent periods. Separate workforce, customer, privileged, and shared device populations so a strong result in one group does not conceal access problems in another.
Quantified benefits should come from verified operational data. Report cost reduction, time saved, or incident changes only when the measurement method and comparison period support the claim.
Capping it Off
Passwordless authentication is an access modernization decision, not simply a change to the login screen. Its value comes from reducing reusable credential exposure while maintaining dependable access and disciplined identity lifecycle management.
The strongest enterprise strategy pairs phishing resistant authentication with secure enrollment, appropriate SSO and MFA policies, controlled recovery, and measured application coverage. Convenience matters, but it should not conceal a weaker path into the same account.
Begin with the accounts and workflows where credential compromise would create the greatest business impact. Validate the operational model, measure results, and expand only when support, recovery, and policy enforcement are ready.
Veritis can help assess identity architecture, define passwordless access policies, and plan application integration through its IAM services. Talk to an IAM consultant to identify the deployment sequence that reduces risk without disrupting business access.