Kubernetes is widely used to deploy and manage applications at scale. It coordinates infrastructure resources for containerized applications and supports workload management through modularity.
Kubernetes supports two update strategies directly through its Deployment API: Recreate and Rolling Update. Blue/green, canary, shadow, and A/B releases are broader deployment patterns that need additional routing, configuration, or delivery tools.
When it is time to deploy production ready containerized apps, choosing a deployment strategy is important. Rolling updates, canary releases, and blue/green deployments can help teams release changes while managing availability and risk. Autoscaling can adjust application capacity as demand changes, but it is separate from the release strategy.
What is Kubernetes Deployment Strategy?
In Kubernetes, a deployment is a resource object that specifies the final state of our program. Deployments are declarative; thus, we don’t specify how the state should achieve them. Instead, we define the desired state and let the deployment controller take over, completing the task automatically to the best of its ability. With Kubernetes deployment tools, we can specify an application’s life cycle, including the images to use, the number of pods to create, and how they should be updated.
A Deployment controller manages ReplicaSets and their pods to match the desired state. A Horizontal Pod Autoscaler (HPA) can separately adjust the desired number of replicas based on workload metrics. Autoscaling complements deployment planning; it does not determine how a new application version is released.
A Kubernetes deployment strategy defines how an application version is introduced, updated, or rolled back. The Deployment API supports Recreate and RollingUpdate. Other approaches, such as canary and blue/green, require additional traffic routing or delivery tooling.
A Kubernetes Deployment manages workload changes, while a Service provides network access to selected pods. Traffic splitting, traffic mirroring, and user cohort routing require appropriate routing configuration or supporting tools.
With Kubernetes deployments, cluster admins can:
- Set up a ReplicaSet or pod.
- Maintain pods and ReplicaSets.
- Revert to previous Deployment revisions.
- Pause or continue rollouts.
For a step by step example of managing Kubernetes applications, see Managing Kubernetes Applications Through Terraform and AWS EKS.
How Kubernetes Deployments Work
A Deployment manages ReplicaSets and pods. Labels and selectors associate resources, while a Service provides a stable endpoint for selected pods. Ingress, Gateway API, or a service mesh can provide additional traffic routing capabilities, depending on the implementation.
| Component | Responsibility | Operational Significance |
| Deployment | Declares replicas, pod templates, and update behavior | Defines the desired workload state |
| Deployment controller | Reconciles the Deployment and its ReplicaSets | Coordinates updates and replica changes |
| ReplicaSet | Maintains a target number of matching pods | Preserves the requested replica count |
| Pod | Runs one or more application containers | Provides the replaceable execution unit |
| Labels and selectors | Associate resources with matching pods | Determine which pods controllers and Services select |
| Service | Provides a stable endpoint for selected pods | Maintains application access while pods change |
| Ingress, Gateway, or service mesh | Provides routing capabilities, depending on implementation | Can enable weighted traffic, cohort routing, or mirroring |
A Service selector that matches pods from both application versions may send traffic to both. Use explicit labels and routing rules when controlling traffic during canary, blue/green, or shadow releases.
Useful link: Managing Kubernetes Applications Through Terraform and AWS EKS
The Best Kubernetes Deployment Strategies
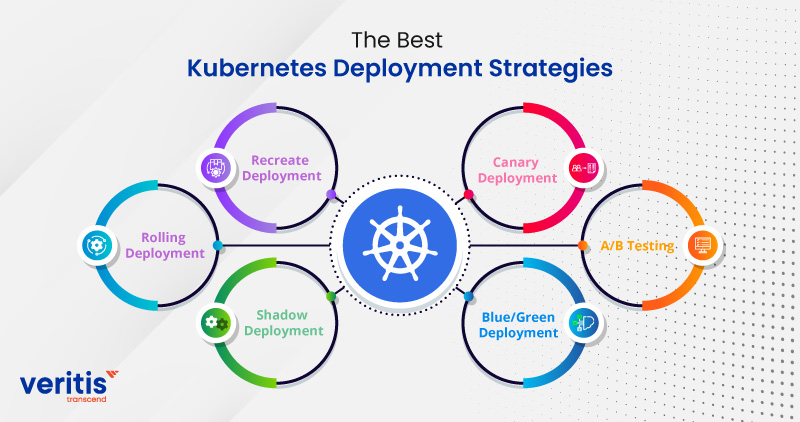
We’ll review several Kubernetes deployment strategies. The Kubernetes Deployment object supports Recreate and RollingUpdate directly. Other release patterns require additional configuration, routing, or tooling. The Kubernetes Deployment documentation explains the supported update behavior.
1) Recreate Deployment
A recreate deployment technique is an all-or-nothing method that instantly lets you update an application with some downtime.
The deployment’s current pods are terminated, and a new version is installed using this technique. Moreover, there is a downtime between when the old version is taken down and when the new pods successfully start up and respond to user queries.
A recreate technique is appropriate for development environments or when users prefer brief downtime over a prolonged period of poor performance or faults.
Recreate deployments are applicable in the following scenarios:
- It is possible to plan maintenance work for off-peak hours, such as weekends, for an application that is only accessed during business hours.
- Due to technological limitations, running two instances of the same software is impossible. You can stop using the older version and only then start the new one with a recreate deployment.
Confirm that storage access, shutdown behavior, and application dependencies support the cutover. Recreate controls Deployment updates, but does not guarantee exclusive operation across every pod or external resource.
2) Rolling Deployment
A RollingUpdate gradually replaces application pods with pods running the new version. It updates the workload in configured batches, not the cluster nodes. Old and new application versions may run concurrently. A single Service can route to both if their labels match its selector; two Services are not required.
A rolling deployment has the benefits of being simpler to implement. Kubernetes retains rollout history that can support a rollback, but the rollback still takes time and does not reverse database changes or other external state. Rolling updates are best suited to applications whose old and new versions can operate together. Validate API, message, and database compatibility before rollout.
The maxUnavailable and maxSurge settings control how many pods may be unavailable or added during an update. Kubernetes documents a default of 25% for both settings; tune them to your availability target and cluster capacity.
3) Shadow Deployment
A shadow deployment mirrors production requests to a new version while the existing version continues responding to users. The shadow version’s responses are not returned to users. Teams can assess performance and stability before deciding whether to expand the release.
Shadow deployments provide the benefit of allowing for the testing of new versions’ non functional features, such as stability and performance. However,
they can be difficult to operate and may require substantial additional capacity, depending on how much traffic is mirrored. Ensure the shadow version cannot trigger duplicate payments, emails, or other side effects, and assess privacy requirements before using production data.
Useful link: How to Optimize Kubernetes Autoscaler to Better Business
4) Blue/Green Deployment
Using a blue/green (or red/black) deployment method, you can deploy a new version without experiencing downtime. Green denotes the new version of the application, while blue denotes the existing one.
Both versions are deployed, but normally only one receives production traffic at a time. While the green deployment is created and tested, traffic continues to the blue deployment. After validation, routing switches to green. The blue deployment can be retained temporarily as a fallback.
A blue/green deployment saves downtime and lowers risk since, if a problem arises during the deployment of the new version, you can roll back to the prior version.
Unfortunately, this tactic can be expensive and needs doubling the resources for both deployments. It also needs a way to quickly switch traffic between the blue and green versions.
A traffic switch does not resolve incompatible database or service changes. Keep the previous version available until the observation period ends, and confirm that shared state and session handling allow a safe rollback.
5) A/B Testing
A/B testing routes user groups to different application versions based on criteria such as cookies, user agents, or other attributes. It can use infrastructure similar to canary deployment, but the purpose differs: A/B testing evaluates a business or user experience hypothesis, while canary deployment primarily limits release exposure and checks operational health.
A/B testing in Kubernetes helps determine which version of the new feature customers prefer before distributing it to all users.
Define the success metric, keep user assignment consistent, and allow enough time to evaluate results before selecting a version.
6) Canary Deployment
A canary deployment method allows you to test a new application version with actual users before rolling it out completely. Initiating a phased deployment entails employing a progressive delivery approach.
A canary technique often involves deploying a new application version to the Kubernetes cluster incrementally while testing it using a limited amount of real world traffic. The prior version available to all other users allows you to test a significant upgrade or experimental feature on a small group of active users.
A common canary setup uses separate stable and canary Deployments, each managing its own ReplicaSet. A routing layer directs a limited share of production traffic to the canary. Teams can increase exposure as confidence grows, or stop and roll back if agreed health signals deteriorate.
Similar to a blue green deployment, there are two key advantages: a Kubernetes application that can run multiple versions simultaneously and a traffic system that can route a portion of requests to the new version.
Define promotion and abort criteria before rollout. Monitor error rates, latency, resource saturation, and critical business transactions. Replica counts alone do not ensure precise traffic percentages because connections and request patterns vary.
For broader context on adoption considerations, see Kubernetes Adoption: The Prime Drivers and Challenges.
Useful link: Kubernetes Adoption: The Prime Drivers and Challenges
How Do Kubernetes Deployment Strategies Compare?
Use the strategy that fits the application’s compatibility, availability, and capacity requirements.
| Strategy | Availability considerations | Capacity considerations | Best fit | Primary caution |
| Recreate | Planned interruption | No full environment overlap required | Incompatible versions or approved maintenance windows | Startup and recovery time |
| RollingUpdate | Can maintain service with suitable configuration | Temporary surge capacity | Routine compatible updates | Old and new versions coexist |
| Shadow | Existing version continues serving users | Extra capacity for mirrored requests | Production workload validation | Duplicate side effects and sensitive data |
| Blue/green | Can support a rapid traffic cutover | Two environments during overlap | Fast switch with a retained fallback | Shared state can undermine rollback |
| A/B testing | Depends on underlying release architecture | Parallel version capacity | Comparing customer outcomes | Cohort consistency and measurement quality |
| Canary | Limits initial user exposure | Stable and canary capacity | Higher risk releases with measurable health gates | Weak telemetry can miss failures |
Choose the simplest strategy that meets the application’s recovery objectives and compatibility constraints. Release decisions should account for customer impact, compliance, staffing, and acceptable infrastructure costs. Veritis can help teams develop a digital strategy that aligns technology decisions with business goals.
Operational Safeguards for Kubernetes Releases
Before production release, validate readiness checks, capacity, routing, and application compatibility. A rollout completing successfully does not prove that customer journeys work correctly. Monitor application telemetry alongside Kubernetes rollout status.
A rollback plan should cover the application image, configuration, database changes, and external side effects. Kubernetes can restore a previous Deployment revision, but does not reverse database updates or restore external resources automatically.
Integrating image provenance, secret handling, access controls, and compatibility checks into DevSecOps implementation makes release assurance more repeatable. Also review resource allocation in Kubernetes clusters to confirm that pods have realistic CPU and memory requests.
Conclusion
The right Kubernetes deployment strategy depends on the application’s availability needs, version compatibility, traffic controls, and recovery requirements. Teams should define health signals and rollback conditions before release, then validate real business transactions during rollout.
Veritis helps organizations plan and manage Kubernetes deployments with release practices aligned to their application and operational requirements. Contact Veritis to discuss your Kubernetes deployment needs.