Organizations recognize the importance of prioritizing a security first approach amid a surge in security breaches. As experts anticipate escalating hacker tactics, adopting a security first mindset becomes indispensable for enterprises across industries. According to a 2026 JPMorgan report, 90% of organizations are progressing through different DevSecOps stages, highlighting its growing adoption.
DevSecOps integrates security processes and automation into the development pipeline, extending modern DevOps methodologies. The phases follow the well known DevOps “infinity loop” structure, adding steps to protect code security before, during, and after deployment to production.
What is DevSecOps?
DevSecOps asserts that everyone is accountable for security and integrates security throughout the Software Development Lifecycle (SDLC). Unlike traditional methods that reserved security for the final stages, DevSecOps phases infuse security into every step. NIST reinforces these phases with updated practices focusing on continuous improvement and AI integration, marking a shift towards more robust security frameworks. Learn more about DevSecOps Best Practices for Security.
Useful link: What is DevSecOps Services?
How to Adopt DevSecOps with Your Team?
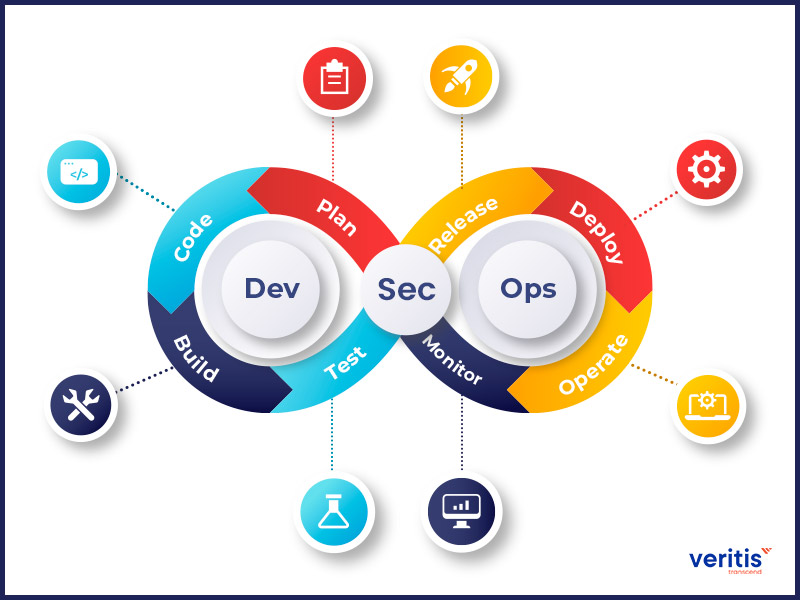
Incorporating security into software development through DevSecOps revolutionizes traditional processes. Here’s how each phase plays a role:
1) Plan
What is the DevSecOps planning phase? The planning phase involves collaboration, discussion, and strategy for security analysis. Teams need thorough security analysis and a detailed security testing schedule.
2) Code
Integrating security tools into the existing Git workflow enables automated security tests with every commit and merge. Tools like PMD, SpotBugs, and Checkstyle facilitate this integration.
3) Build
This stage automates security analysis of the build output. Static application software testing (SAST) and software composition analysis are critical. The build phase relies on tools such as Checkmarx and SonarQube for effective security checks.
4) Test
The test phase uses dynamic application security testing (DAST) tools to identify vulnerabilities. Tools like OWASP ZAP and AppScan play a crucial role during this stage.
5) Release
The release phase focuses on protecting runtime environments by reviewing configurations and access control. Implementation of policies like the principle of least privilege (PoLP) is essential here.
6) Deploy
During deployment, ensure that production environments match staging settings. Runtime verification tools like Osquery and Falco help ensure systems align with intended functions.
7) Operation
Operations involve ongoing maintenance and monitoring for zero day vulnerabilities, a critical component in a robust DevSecOps framework.
8) Monitor
Continuous monitoring prevents breaches by identifying anomalies early. This phase is crucial for maintaining a secure environment through real time monitoring tools.
Useful link: DevSecOps Solution to Cloud Security Challenge
DevSecOps Tools, Activities, and Automation by Phase
Here’s a tactical breakdown of tools, activities, and automated security gates across each phase of the DevSecOps methodology:
| Phase | Key Activities | Tools and Frameworks | Automation Gates |
| Plan | Define threats, business risks | IriusRisk, ThreatModeler | Security goals validated before kickoff |
| Design | Threat modeling, architectural risk analysis | Microsoft SDL, OWASP Threat Dragon | Architecture is approved only if secure |
| Code | SAST, secret scanning, secure coding | SonarQube, GitGuardian, ESLint | Block commits with critical issues |
| Build | SCA, binary validation, SBOM generation | Snyk, OWASP Dependency Check, Syft | Fail build on vulnerable dependencies |
| Test | DAST, IAST, API testing | OWASP ZAP, Burp Suite, Postman Security | Require full coverage and pass on criticals |
| Release | Native mobile testing | Checkov, Terraform Validator, Trivy | Fail pipeline on misconfigurations |
| Deploy | Least privilege enforcement, container hardening | KICS, Polaris, Kube bench | Block deploys without passing security checks |
| Operate | Runtime protection, incident detection | Falco, GuardDuty, Sysdig Secure | Alert and auto remediate runtime threats |
| Monitor | SIEM, anomaly detection, metrics tracking | Datadog, Splunk, New Relic | Trigger investigations on unusual behavior |
| Feedback | Audit, lessons learned, continuous improvement | Jira, Confluence, Retrospective Frameworks | Feed issues into new sprints |
Benefits of DevSecOps
What are the key benefits of DevSecOps? Integrating security into DevOps offers several benefits that affect speed, collaboration, and cost. Key advantages include:
1) Rapid Vulnerability Mitigation: Automating vulnerability scanning into the release cycle enables quick detection and resolution.
2) Shared Responsibility: Teams align early in the development cycle, fostering collaboration and minimizing conflicts.
3) Enhanced Application Security: Proactively addressing vulnerabilities leads to robust security throughout the lifecycle.
4) Cost Efficient Software Delivery: Integrating security early reduces the need for costly rework and reviews.
Ensure Regulatory Compliance
How does DevSecOps ensure regulatory compliance? By integrating security assessments and testing into each development phase, DevSecOps helps organizations adhere to regulatory standards such as GDPR and HIPAA. This proactive approach avoids after the fact security adjustments that could lead to compliance violations and significant fines.
DevSecOps Best Practices
Adopting DevSecOps involves several best practices, including protecting production environments, implementing Role Based Access Control (RBAC), and ensuring secure application development processes. Integrating Two Factor Authentication (2FA) and securing sensitive information enhances overall security.
Implementing DevSecOps Challenges
Challenges in adopting DevSecOps include addressing vulnerabilities, managing the complexity of cloud environments, and overcoming compatibility issues with various open source tools. For further insights, visit the DevSecOps for Cloud Security Challenge.
Useful link: Pros and Cons of DevSecOps
DevSecOps vs. SecDevOps vs. DevOps: What is the Difference?
While DevOps focuses on integrating development and operations, DevSecOps incorporates security from the start. SecDevOps emphasizes security at every stage of the process. Recognizing these distinctions can help your organization choose the most suitable approach.
Key Insights
Key insights for implementing DevSecOps include the following:
- Cultural Shift: DevSecOps requires a cultural shift where security is a shared responsibility.
- Automation: Automation is essential for maintaining efficiency and security across all stages.
- Continual Learning: Continuous training and adaptation are vital as security threats evolve.
DevSecOps Security Monitoring
How crucial is security monitoring in DevSecOps? Organizations must continuously monitor live applications for security threats. Tools like Runtime Application Self Protection (RASP) help in real time threat detection and response. Real time monitoring tools ensure that potential threats are identified and mitigated swiftly.
Conclusion
As the importance of security grows, adopting DevSecOps becomes crucial. By embedding security into every phase, organizations strengthen their development processes, foster a culture of security, and reduce vulnerabilities. Discover more about DevSecOps Solutions for Security Challenges.